
CISSP-116 · Lesson 8 of 12 · 28 min
Incident reporting: legal, regulatory and law enforcement obligations
When an incident involves personal information, regulated data, a public company or critical infrastructure, the organization will usually have legal duties to report it: to a regulator, to affected individuals, to investors, to customers under contract, or to a national cyber agency. These duties have their own definitions, thresholds and deadlines, and missing them can turn a manageable incident into an enforcement action. Reporting is therefore a core part of incident management, and the incident response plan must build the legal assessment into the process from the first hours.
This lesson maps the main obligations in Canada and the United States as of October 2026 and explains how to run the reporting decision as a process. CISSP-113 covered the broader legal and regulatory landscape, privacy principles and the governance of compliance; this lesson focuses on what happens to those obligations when an incident occurs.
Running the reporting decision as a process
Reporting duties typically turn on three questions: what happened (for example, unauthorized access to or disclosure of personal information), how serious it is (a harm threshold or materiality test), and when the clock started (often at discovery or at a determination that the threshold is met). Because these are legal judgments made on incomplete facts, the plan should assign a named person, usually the privacy officer working with counsel, to run a documented assessment as soon as an incident might involve regulated data. Every decision, including a decision not to report, should be recorded with the facts known at the time and the reasoning.
| Step | Question | Who leads |
|---|---|---|
| 1. Identify | Does the incident involve personal information, regulated data, a listed company or a regulated sector? | Incident manager flags; privacy officer confirms |
| 2. Scope | Whose data, how many people, which jurisdictions, what types of data? | Security analysts with data owners |
| 3. Assess threshold | Does it meet each applicable test (harm, materiality, reportable incident)? | Privacy officer and counsel |
| 4. Determine clocks | When did each clock start, and what is each deadline? | Counsel |
| 5. Notify | Prepare required content for each regulator, individual or agency | Privacy, legal and communications |
| 6. Record | Document the assessment, decisions and notices, and update as facts change | Privacy officer |
Multi-jurisdiction incidents are common: a Canadian company with US customers, or a US company with employees in Quebec, may face several sets of rules at once, each with different triggers and deadlines. A jurisdiction table prepared in advance, listing the rules that apply to the organization's data and the information each notice requires, saves time when the clock is running.
Privacy breach reporting
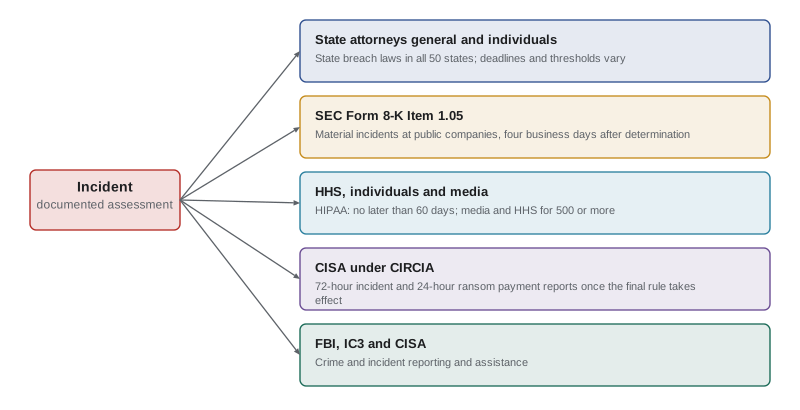
In the United States there is no single federal breach notification law for most personal information. Instead, all 50 states, the District of Columbia, Puerto Rico, Guam and the US Virgin Islands have breach notification laws. They differ in what counts as personal information (most include a name with a Social Security number, driver's license or account number with access code, and many now include biometric, health or online credentials), in whether a risk-of-harm analysis can avoid notification, and in timing: some require notice in the most expedient time possible and without unreasonable delay, while others set specific outer limits such as 30, 45 or 60 days. Many states also require notice to the state attorney general once a threshold number of residents, often 500 or 1,000, is affected, and to consumer reporting agencies for larger breaches. The rules of every state where affected individuals live apply, not just the organization's home state.
Sector rules add to the state laws. The Gramm-Leach-Bliley Act Safeguards Rule, as amended by the Federal Trade Commission, requires non-bank financial institutions to notify the FTC within 30 days of discovering a notification event involving the unencrypted information of at least 500 consumers. Federal banking regulators require banks to notify their primary regulator within 36 hours of determining that a significant computer-security incident has occurred. The FTC's Health Breach Notification Rule covers many health apps that fall outside HIPAA. Contracts with customers and payment card brands often impose their own, shorter notice periods.
Comprehensive state privacy laws, such as the California Consumer Privacy Act as amended by the California Privacy Rights Act, add a private right of action for certain data breaches caused by a failure to maintain reasonable security, which raises the litigation stakes of an incident. Organizations should therefore keep an internal register of all security incidents involving personal information, including those assessed as not notifiable, with the reasoning. Some state laws require documentation of a no-harm determination to be kept for several years, and regulators routinely ask to see it.
Health and financial sector reporting
Under the HIPAA Breach Notification Rule, covered entities must notify affected individuals without unreasonable delay and no later than 60 calendar days after discovering a breach of unsecured protected health information. For breaches affecting 500 or more residents of a state or jurisdiction, they must also notify prominent media outlets and the Secretary of Health and Human Services within the same period; smaller breaches are logged and reported to HHS within 60 days after the end of the calendar year. Business associates must notify the covered entity. Encryption that meets HHS guidance means the information is not unsecured, which is one of the strongest arguments for encrypting health data.
Public companies are subject to the SEC's cybersecurity disclosure rules adopted in July 2023. Under Form 8-K Item 1.05, a registrant must disclose a cybersecurity incident it determines to be material within four business days of that determination, describing the nature, scope and timing of the incident and its material impact or reasonably likely impact. The materiality determination must be made without unreasonable delay after discovery. Disclosure can be delayed only if the US Attorney General determines that it would pose a substantial risk to national security or public safety. Companies must also describe cyber risk management and governance annually under Regulation S-K Item 106. Many organizations therefore have a disclosure committee that receives incident escalations so that materiality can be assessed promptly.
Critical infrastructure reporting
The Cyber Incident Reporting for Critical Infrastructure Act of 2022 (CIRCIA) will require covered entities in critical infrastructure sectors to report covered cyber incidents to CISA within 72 hours of reasonably believing one has occurred, and ransom payments within 24 hours, once CISA's final rule takes effect. CISA published a proposed rule in April 2024 and sent the final rule to the Office of Management and Budget for review on 1 October 2026; it had not been published as of mid-October 2026, and until it takes effect reporting under CIRCIA is voluntary (checked October 2026). Sector regulators, such as the Transportation Security Administration for pipelines and rail, already require reporting to CISA within short periods.
Law enforcement and national agencies
In the United States, organizations can report cybercrime to their local FBI field office and through the FBI's Internet Crime Complaint Center (IC3), and report incidents to CISA, which offers technical assistance and shares indicators with other defenders. The US Secret Service also investigates cyber-enabled financial crime. Under CIRCIA, a report to CISA is not a report to the privacy regulators or the SEC; those duties remain separate. Before sharing evidence with law enforcement, organizations should agree with counsel what is provided and how chain of custody will be maintained, as Lesson 2 described.
Engaging law enforcement early has benefits: investigators may already know the adversary, may be able to help recover funds in fraud cases if contacted within hours, and may provide threat information. Involving them does not mean surrendering control of the response, and law enforcement in both countries generally works to minimize disruption to victims. In some cases investigators may ask an organization to delay public notification to protect an investigation; most notification laws allow for that delay when requested by law enforcement, but the request should be documented.
Calculating deadlines
Deadlines expressed in hours, calendar days or business days, starting from different trigger points, are easy to miscalculate under pressure. A simple calculator, maintained by counsel and included in the plan, helps the incident manager see all the clocks on one page.
from datetime import date, datetime, timedelta
# Notification clocks for one synthetic incident; triggers and deadlines vary by rule and need legal advice
holidays = {date(2026, 11, 11), date(2026, 11, 26)}
def add_business_days(d, n):
    while n:
        d += timedelta(days=1)
        if d.weekday() < 5 and d not in holidays:
            n -= 1
    return d
discovered = date(2026, 11, 6)                       # Friday
significant_determined = datetime(2026, 11, 6, 15, 0)
materiality_determined = date(2026, 11, 10)          # Tuesday
clocks = [
    ('Banking regulator, 36 hours from determination (US)', (significant_determined + timedelta(hours=36)).strftime('%Y-%m-%d %H:%M')),
    ('SEC 8-K Item 1.05, 4 business days after materiality (US)', add_business_days(materiality_determined, 4).isoformat()),
    ('GLBA Safeguards, FTC notice within 30 days (US)', (discovered + timedelta(days=30)).isoformat()),
    ('HIPAA outer limit, 60 calendar days (US)', (discovered + timedelta(days=60)).isoformat()),
    ('PIPEDA, as soon as feasible (Canada)', 'no fixed day: act promptly'),
]
for name, due in clocks:
print(f'{name:58s} {due}')Banking regulator, 36 hours from determination (US) 2026-11-08 03:00 SEC 8-K Item 1.05, 4 business days after materiality (US) 2026-11-17 GLBA Safeguards, FTC notice within 30 days (US) 2026-12-06 HIPAA outer limit, 60 calendar days (US) 2027-01-05 PIPEDA, as soon as feasible (Canada) no fixed day: act promptly
Note that the SEC deadline skips the weekend and a US federal holiday, and that rules phrased as as soon as feasible or without unreasonable delay have no safe harbor date: regulators expect organizations to move as fast as the facts allow, and outer limits are maximums, not targets.
# A structured real-risk-of-significant-harm style assessment (illustrative scoring, not a legal test)
sensitivity = {'contact details': 1, 'account number': 2, 'government ID': 3, 'health information': 3, 'credentials': 3}
probability = {'encrypted, key safe': 0, 'lost device, no evidence of access': 1, 'sent to wrong trusted recipient, confirmed deleted': 0,
               'accessed by unknown party': 2, 'posted publicly or ransomed': 3}
cases = [
    ('Laptop lost, full disk encryption on', 'government ID', 'encrypted, key safe'),
    ('Email with health details sent to wrong clinic, deleted', 'health information', 'sent to wrong trusted recipient, confirmed deleted'),
    ('Customer portal accessed with stolen passwords', 'account number', 'accessed by unknown party'),
    ('HR files posted on extortion site', 'government ID', 'posted publicly or ransomed'),
]
for desc, data, prob in cases:
    s, p = sensitivity[data], probability[prob]
    verdict = 'likely notifiable: consult counsel' if s * p >= 4 else ('borderline: document and consult counsel' if s * p >= 2 else 'likely not notifiable: record it')
print(f'{desc:55s} sensitivity {s} x probability {p} = {s*p} {verdict}')Laptop lost, full disk encryption on sensitivity 3 x probability 0 = 0 likely not notifiable: record it Email with health details sent to wrong clinic, deleted sensitivity 3 x probability 0 = 0 likely not notifiable: record it Customer portal accessed with stolen passwords sensitivity 2 x probability 2 = 4 likely notifiable: consult counsel HR files posted on extortion site sensitivity 3 x probability 3 = 9 likely notifiable: consult counsel
The scoring is a way of documenting thinking, not a legal test, and counsel should review any borderline case. Even incidents assessed as not notifiable must be recorded: in Canada under the PIPEDA 24-month record-keeping rule and the Law 25 register, and in the United States in an internal register that regulators may request.
Worked problem
One incident, several duties
A company listed on both the Toronto Stock Exchange and Nasdaq discovers that an attacker accessed a database holding names and health insurance numbers of 3,200 employees in Ontario, Quebec and Texas.
Show solution
- Privacy officer and counsel open a documented assessment on the day of discovery.
- Canada: assess real risk of significant harm under PIPEDA (or the applicable provincial law for employee data) and risk of serious injury under Quebec Law 25; health and government identifiers are sensitive and access by an unknown party makes misuse probable, so report and notify as soon as feasible and add the incident to the PIPEDA record and Law 25 register.
- United States: check the Texas breach law, which sets a 60-day outer limit for individual notice and requires notice to the attorney general when 250 or more Texans are affected.
- Disclosure committee assesses materiality for the SEC and Canadian securities rules; if material, file Form 8-K Item 1.05 within four business days of the determination.
- Report the crime to police and the RCMP NC3, the FBI or IC3, and inform CCCS and CISA, agreeing with counsel on evidence sharing.
Answer: Run a single documented assessment that tracks each jurisdiction's test and clock, then send each required notice with consistent facts.
Common mistakes
MistakeWaiting until the investigation is complete before considering reporting duties.
InsteadStart a documented legal assessment as soon as regulated data might be involved, because clocks may already be running.
MistakeRecording only the breaches that are reported.
InsteadRecord every breach of security safeguards with the reasoning, as PIPEDA, Law 25 and US regulators expect.
MistakeApplying only the home jurisdiction's rules.
InsteadApply the rules where affected individuals live and where the organization is regulated.
MistakeTreating an outer limit such as 60 days as the target.
InsteadNotify as soon as the facts allow; outer limits are maximums.
MistakeAssuming a report to a national cyber agency satisfies privacy or securities duties.
InsteadTreat each regulator's duty separately.
MistakeSending inconsistent facts to different regulators and the public.
InsteadMaintain one fact base, reviewed by counsel, for all notices.
Summary and key terms
- Reporting duties depend on what happened, a seriousness threshold and when the clock started; assess them from the first hours.
- Canada: PIPEDA requires reporting to the OPC and notice to individuals when there is a real risk of significant harm, and records of all breaches for 24 months.
- Quebec Law 25 requires notice for incidents presenting a risk of serious injury and a register of all confidentiality incidents.
- United States: every state has a breach law; HIPAA allows no more than 60 days; SEC Form 8-K Item 1.05 requires disclosure within four business days of a materiality determination.
- Canada's Critical Cyber Systems Protection Act (Bill C-8) and the US CIRCIA will add critical infrastructure reporting once their regulations or final rule take effect.
- Law enforcement contacts include police and the RCMP NC3 with CCCS in Canada, and the FBI, IC3 and CISA in the United States.
- Document every decision and keep facts consistent across all notices.
- RROSH
- Real risk of significant harm: the PIPEDA threshold for reporting a breach of security safeguards.
- Breach of security safeguards
- Under PIPEDA, loss of, unauthorized access to or unauthorized disclosure of personal information resulting from a breach of safeguards or a failure to establish them.
- Confidentiality incident
- The Quebec Law 25 term for unauthorized access, use, communication or loss of personal information.
- Breach record
- The record of every breach of security safeguards that PIPEDA requires organizations to keep for 24 months.
- Materiality
- Whether information would be important to a reasonable investor; the test for SEC incident disclosure.
- Form 8-K Item 1.05
- The SEC disclosure item for material cybersecurity incidents, due within four business days of determining materiality.
- Unsecured PHI
- Protected health information not rendered unusable to unauthorized persons, for example by encryption, under HIPAA.
- CIRCIA
- The US Cyber Incident Reporting for Critical Infrastructure Act of 2022.
- Critical Cyber Systems Protection Act
- The Canadian law enacted by Bill C-8 that imposes cyber security program and reporting duties on designated operators.
- NC3
- The RCMP national cybercrime coordination unit, which runs Canada's online cybercrime reporting system.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What three questions do most reporting duties turn on?
Show answer
What happened, whether it meets a seriousness threshold and when the clock started.
What is the PIPEDA threshold for reporting a breach?
Show answer
A real risk of significant harm to an individual.
What two factors does PIPEDA use to assess real risk?
Show answer
Sensitivity of the information and probability of misuse.
How long must PIPEDA breach records be kept?
Show answer
24 months after the day the breach was determined to have occurred.
What must Quebec organizations keep under Law 25?
Show answer
A register of all confidentiality incidents.
What is the outer limit for HIPAA individual notice?
Show answer
60 calendar days after discovery.
When must a material incident be disclosed on Form 8-K?
Show answer
Within four business days of determining that it is material.
What is the status of CIRCIA reporting as of October 2026?
Show answer
The final rule was sent to OMB on 1 October 2026 and had not taken effect; reporting under CIRCIA was voluntary.
Name the Canadian and US agencies for reporting cybercrime.
Show answer
Canada: police and the RCMP NC3 with CCCS; United States: the FBI, IC3 and CISA.
Why should incidents assessed as not notifiable still be recorded?
Show answer
Laws and regulators expect a record of all breaches with the reasoning, and may ask to see it.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.