
CISSP-110 · Lesson 4 of 12 · 26 min
Cybercrime, intellectual property and export controls in Canada and abroad
Sub-domain 1.4 asks you to understand legal, regulatory and compliance issues in a holistic context. In practice that means knowing the main categories of law that affect security work, recognizing which questions need a lawyer, and understanding that an organization operating across borders may face several legal systems at once. This lesson covers cybercrime and data breaches, intellectual property and licensing, and import and export controls. Lesson 5 covers privacy and transborder data flows, and Lesson 6 covers contracts, compliance and investigations.
Categories of law
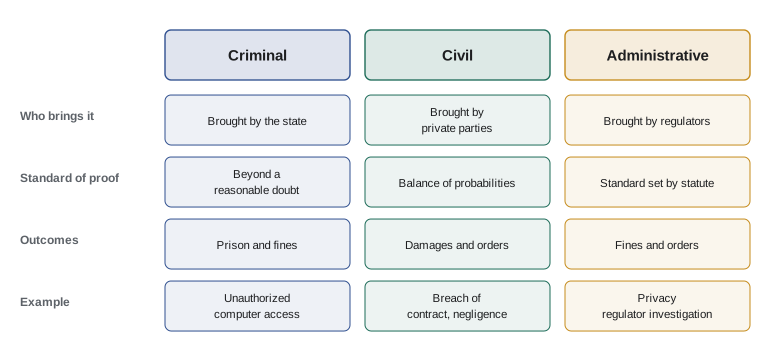
Security professionals meet three broad categories of law. Criminal law deals with offences against society, prosecuted by the state, with penalties that can include imprisonment; the standard of proof is beyond a reasonable doubt. Civil law deals with disputes between private parties, such as breach of contract or negligence, and remedies are usually money damages or orders; the standard is the balance of probabilities, sometimes called the preponderance of the evidence. Administrative or regulatory law is made and enforced by government agencies under authority from legislation, such as privacy regulators, securities commissions and financial supervisors; it can bring fines, orders and licence conditions.
Legal systems also differ. Canada, apart from Quebec's private law, and the United States use common law, in which court decisions create binding precedent alongside legislation. Quebec and most of continental Europe use civil law systems based on comprehensive codes. Some countries use religious or customary law, or mixtures. When an organization operates internationally, contracts usually specify which jurisdiction's law governs and where disputes will be heard.
Cybercrime
Most countries criminalize unauthorized access to computers, interference with data, and misuse of devices or passwords. Attacks often cross borders, which makes investigation and prosecution hard: the attacker, the victim, the servers and the stolen data may all be in different countries. International cooperation relies on mutual legal assistance treaties and on the Council of Europe Convention on Cybercrime (the Budapest Convention, 2001), which harmonizes offences and procedures among its parties, including Canada and the United States. A United Nations Convention against Cybercrime was adopted by the General Assembly in December 2024 and opened for signature in 2025; it will take effect only after enough states ratify it, and many security and human rights groups have criticized its broad scope.
In Canada, the main cybercrime provisions are in the Criminal Code. Section 342.1 makes unauthorized use of a computer an offence, including obtaining computer services fraudulently, intercepting functions of a computer and using a computer to commit other offences. Section 342.2 covers possessing or distributing devices designed primarily for those offences. Section 430(1.1) creates the offence of mischief in relation to computer data, which covers destroying, altering or interfering with data. Section 184 criminalizes interception of private communications, and identity theft and identity fraud are covered in sections 402.2 and 403. Incidents can be reported to local police and to the Canadian Anti-Fraud Centre, and the Canadian Centre for Cyber Security accepts incident reports from organizations.
Data breach law sits between criminal and regulatory law. When personal information is exposed, organizations often have legal duties to notify regulators and affected individuals, whatever the cause. Lesson 5 covers breach notification rules in detail, because they are mainly part of privacy law. From a governance view, the key point is that the organization that held the data is responsible for the breach response even when a criminal caused it.
Intellectual property
Intellectual property (IP) is often an organization's most valuable information asset. Security programs protect it, and security professionals must also respect others' IP, for example by complying with software licences. The four main types are copyright, trademarks, patents and trade secrets.
| Type | Protects | How obtained | Typical term |
|---|---|---|---|
| Copyright | Original expression, including software code and documentation | Automatic on creation; registration optional | Canada and US: generally life of the author plus 70 years |
| Trademark | Names, logos and marks that identify the source of goods or services | Use, strengthened by registration | Renewable indefinitely while in use (10-year renewals) |
| Patent | Novel, useful and non-obvious inventions | Application and examination | Generally 20 years from filing |
| Trade secret | Valuable information kept confidential, such as formulas and source code | Reasonable steps to keep it secret | As long as secrecy is maintained |
Trade secrets deserve special attention from security leaders, because their legal protection depends on the owner taking reasonable measures to keep them secret. Access controls, classification labels, non-disclosure agreements, exit interviews and monitoring of data transfers are not only good practice; they are evidence that the organization treated the information as secret if it ever has to go to court.
In Canada, copyright is governed by the Copyright Act, which extended the general term to life of the author plus 70 years from 30 December 2022, without reviving expired works; it also prohibits circumventing technological protection measures, with exceptions such as security research and interoperability. Trademarks are registered with the Canadian Intellectual Property Office (CIPO) under the Trademarks Act, and patents under the Patent Act. Canada has no single trade secret statute; protection comes from common law and equity (breach of confidence), contracts and, in Quebec, the Civil Code, and the Criminal Code was amended in 2020 to add a trade secret offence (section 391).
Licensing
Software is usually licensed rather than sold: the buyer gets rights to use it under conditions. Common models include perpetual licences, subscriptions, per-user and per-core licensing, site licences, and open-source licences ranging from permissive (MIT, Apache 2.0, BSD) to copyleft (GPL), which requires derivative works distributed to others to be released under the same terms. Click-through and shrink-wrap licences are generally enforceable if users had a reasonable chance to see the terms.
Licence management is a security and compliance issue. Unlicensed software can bring legal claims and audits from vendors or industry groups; unmanaged open-source components can bring both licence obligations and security vulnerabilities. A software bill of materials (SBOM), discussed in Lesson 10, helps track what components are in use and under which licences. Software asset management tools and clear procurement policies keep usage within licensed limits.
Worked problem
A licence audit
A vendor audit finds 420 installations of a design tool licensed for 300 users. The list price is $1,200 per licence per year, and the contract allows the vendor to bill unlicensed use at list price for the past two years plus a 15 per cent penalty. Estimate the exposure and the governance lesson.
Show solution
- Unlicensed installations: \( 420 - 300 = 120 \).
- Back-billing for two years: \( 120 \times 1200 \times 2 = 288{,}000 \).
- Penalty: \( 0.15 \times 288{,}000 = 43{,}200 \).
- Total exposure: \( 288{,}000 + 43{,}200 = 331{,}200 \) dollars, before negotiation.
Answer: About $331,000. The governance lesson is to control installation rights, track licences against use and include software asset management in the security and procurement programs.
Import and export controls
Many countries control the export of certain technologies, including some encryption products, intrusion software and items with military uses. Controls apply not only to shipping hardware but also to transferring software and technical data electronically, and sometimes to sharing controlled technical information with foreign nationals inside the country, which the US calls a deemed export. Multilateral regimes coordinate these controls. The Wassenaar Arrangement, with 42 participating states including Canada and the United States, maintains lists of dual-use goods and technologies, including categories for information security items.
In Canada, export controls are administered by Global Affairs Canada under the Export and Import Permits Act. The Export Control List, which incorporates the Wassenaar lists, identifies controlled items, and Group 1 Category 5 Part 2 covers information security items such as some cryptography. Many mass-market encryption products are released from control, but specialized products may need a permit. Canada also maintains economic sanctions against certain countries and persons under the Special Economic Measures Act and related laws, and the Controlled Goods Program, run by Public Services and Procurement Canada, regulates access to controlled military goods and technical data in Canada.
Import controls also matter. Some countries restrict the import or use of encryption, require registration of cryptographic products, or require access to keys. Before sending staff abroad with encrypted laptops, or deploying products in a new country, security teams should check both export rules at home and import rules at the destination.
Worked problem
Travelling with encrypted laptops
An engineering team is travelling to a trade show in another country with laptops containing controlled technical drawings and full-disk encryption. What should the security manager check?
Show solution
- Export: are the drawings controlled technical data that need a permit or licence to take abroad?
- Encryption: does the laptop encryption qualify for a mass-market release or licence exception?
- Import: does the destination restrict encryption or require disclosure of keys at the border?
- Alternative: issue clean loaner laptops with only the data needed, and access the rest remotely through approved channels if lawful.
Answer: Check export controls on the data and encryption, import rules at the destination and sanctions, and consider loaner devices to reduce exposure.
Working with law enforcement and counsel
Deciding whether to involve law enforcement after a cybercrime is a business decision that should be planned before an incident. Benefits include access to intelligence about the attackers, the possibility of recovering funds or decryption keys, and support for prosecution. Concerns include loss of control over the timeline, disclosure of sensitive information and the time staff must spend supporting the investigation. Many organizations decide in their incident response plan which kinds of incidents they will report, and build relationships with police cybercrime units and national cyber centres in advance.
Legal counsel should be involved early in any significant incident. Counsel can advise on notification duties, contractual obligations, evidence preservation and communications, and can direct forensic investigations in a way that may protect sensitive findings under privilege. Security leaders should know which outside law firms and forensic providers the organization will call, whether its cyber insurer requires specific panel firms, and who has authority to engage them at short notice. Ransom payments raise further legal questions, including sanctions laws that can make paying certain groups illegal, and most governments discourage paying at all.
Contracts with suppliers and customers often address these legal topics directly: who owns the intellectual property in work product, which country's law governs, how export-controlled data must be handled, and what each party must do if a cybercrime affects shared systems. Security leaders should review such clauses with counsel, because they shape responsibilities long before any incident occurs.
Common mistakes
MistakeAssuming cybercrime law is the same everywhere.
InsteadOffences, procedures and evidence rules differ; cooperation relies on treaties such as the Budapest Convention.
MistakeTreating trade secrets as protected automatically.
InsteadProtection depends on reasonable steps to keep the information secret.
MistakeForgetting that copyright protects code but not ideas.
InsteadCopyright covers expression; patents may protect inventions.
MistakeThinking export controls apply only to physical shipments.
InsteadElectronic transfers and sharing with foreign nationals can also be exports.
MistakeIgnoring open-source licence terms.
InsteadCopyleft licences impose obligations; track components with an SBOM.
Summary and key terms
- Criminal, civil and administrative law differ in who brings the case, the standard of proof and the penalties.
- Common law and civil law systems differ; contracts specify governing law and jurisdiction.
- Computer crime laws criminalize unauthorized access, data interference and misuse of devices; cross-border cases rely on treaties.
- Copyright, trademarks, patents and trade secrets protect intellectual property in different ways and for different terms.
- Trade secret protection depends on reasonable security measures.
- Software licences, including open-source licences, carry obligations that need active management.
- Export controls, coordinated through the Wassenaar Arrangement, cover some encryption and technical data; import rules vary by country.
- Criminal law
- Law dealing with offences against society, prosecuted by the state.
- Civil law (tort and contract)
- Law resolving disputes between private parties, usually by damages.
- Administrative law
- Rules made and enforced by government agencies under legislation.
- Budapest Convention
- The Council of Europe treaty harmonizing cybercrime laws and cooperation.
- Copyright
- Protection of original expression, arising automatically on creation.
- Trademark
- Protection of marks identifying the source of goods or services.
- Patent
- Protection of novel, useful and non-obvious inventions for a limited term.
- Trade secret
- Valuable information protected by keeping it confidential.
- Copyleft
- An open-source licence condition requiring derivatives to use the same licence.
- Wassenaar Arrangement
- A multilateral regime coordinating export controls on dual-use goods and technologies.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What standard of proof applies in criminal cases?
Show answer
Beyond a reasonable doubt.
Which treaty harmonizes cybercrime laws among Canada, the US and many others?
Show answer
The Budapest Convention on Cybercrime.
Which type of IP lasts as long as secrecy is maintained?
Show answer
Trade secret.
What is the general copyright term in Canada and the US?
Show answer
Life of the author plus 70 years.
What does a copyleft licence require?
Show answer
Distributed derivative works must be released under the same licence.
Name the multilateral regime for dual-use export controls.
Show answer
The Wassenaar Arrangement.
Can sharing technical data with a foreign national at home be an export?
Show answer
Yes, under some rules such as US deemed exports.
Why are NDAs and access controls important for trade secrets?
Show answer
They show reasonable steps to keep the information secret.
Which category of law covers a privacy regulator's fine?
Show answer
Administrative (regulatory) law.
What tool helps track open-source components and licences?
Show answer
A software bill of materials (SBOM).
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.