
CISSP-111 · Lesson 9 of 12 · 27 min
Retention, legal holds and records management in Canada
Keeping data too briefly can break the law, lose evidence and harm the business. Keeping it too long can also break the law, multiply the damage from a breach and drive up storage and discovery costs. Retention is the discipline of keeping each kind of information for the right period and then disposing of it properly. The 2024 outline includes data retention in the data life cycle (sub-domain 2.4) and asset retention in sub-domain 2.5. This lesson covers retention schedules, the legal and regulatory minimums and maximums that shape them, legal holds, records management, and how to make disposal happen in practice.
Why retention matters for security
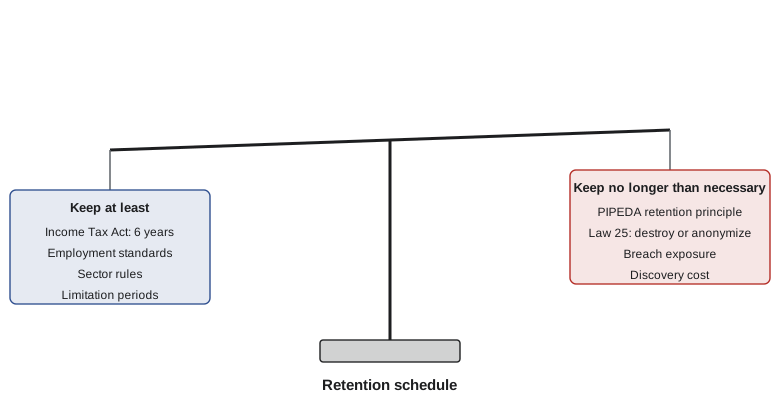
Every record kept beyond its useful life is a liability with no matching benefit. Breach reports regularly reveal attackers stealing years of old customer records that no one needed: former customers, unsuccessful applicants, expired accounts. Over-retention increases notification costs, fines and lawsuits after a breach, makes privacy access requests harder to answer, and increases the cost of electronic discovery in litigation, where every relevant record held must be searched and possibly produced. Under-retention has its own costs: tax penalties, inability to defend claims, regulatory sanctions and, if records are destroyed when litigation is expected, accusations of spoliation of evidence. A good retention program balances these risks deliberately.
The retention schedule
A retention schedule, sometimes called a records retention schedule or disposition schedule, lists categories of records, how long each must be kept, the event that starts the clock, the legal or business reason, the owner, and what happens at the end: destruction, transfer to an archive or review. Records are grouped into categories such as employee files, customer contracts, invoices, tax records, system logs and marketing lists, so that the schedule stays manageable. The trigger event matters as much as the period: seven years from the end of the fiscal year, two years after an employee leaves, one year after the last customer transaction.
| Record category | Trigger | Period | Basis | Disposition |
|---|---|---|---|---|
| Accounting and tax records | End of tax year | 7 years (illustrative, above legal minimums) | Tax law and audit | Destroy with certificate |
| Employee personnel files | Termination | 3 years | Employment standards, claims | Destroy |
| Unsuccessful job applications | Hiring decision | 1 year | Defend complaints, privacy | Destroy |
| Customer contracts | Contract end | Limitation period plus margin | Contract claims | Destroy or archive |
| Security logs | Creation | 1 year online, longer archived | Investigations, standards | Delete |
| Board minutes | Creation | Permanent | Corporate law, history | Archive |
Setting periods requires input from legal counsel, records managers, the business owners of each category, privacy and security. The schedule should be approved by senior management, published, reviewed at least every few years and whenever laws change, and applied to all formats and locations, including email, chat, cloud services and backups.
Legal minimums
In Canada, the Income Tax Act generally requires businesses to keep books and records, including supporting documents, for six years from the end of the last tax year to which they relate, longer if an assessment is under objection or appeal, and the Canada Revenue Agency applies the same period for GST/HST records. Provincial employment standards laws set minimums for payroll and employment records; Ontario's Employment Standards Act, 2000, for example, generally requires employers to keep many records for three years. Corporate statutes require minute books and shareholder registers to be kept for the life of the corporation. Regulated sectors add their own rules: securities dealers under CIRO rules, banks under OSFI guidance and the Proceeds of Crime (Money Laundering) and Terrorist Financing Act, which requires many records for at least five years, and health records under provincial laws and professional college standards, often ten years or more after the last visit, longer for minors.
Legal minimums vary by jurisdiction, industry and record type, and a multinational organization usually adopts the longest applicable minimum for each category unless privacy rules require something shorter. The schedule should cite the source of each period so that it can be checked and updated.
Legal maximums and privacy
Privacy law sets the other side of the balance. PIPEDA's limiting use, disclosure and retention principle requires organizations to keep personal information only as long as necessary to fulfil the identified purposes, to develop guidelines and procedures for retention, and to destroy, erase or anonymize information that is no longer required. Where personal information is used to make a decision about an individual, it must be kept long enough to allow the person to access it. Organizations must keep records of all breaches of security safeguards for 24 months. Quebec's Law 25 requires that personal information be destroyed or anonymized once the purpose of collection is achieved, subject to retention periods set by law, and allows anonymized information to be used only for serious and legitimate purposes under conditions set by regulation.
Internationally, the GDPR's storage limitation principle requires that personal data be kept in identifiable form no longer than necessary for the purposes for which it is processed. The common thread is clear: retention must be justified by a purpose, and when the purpose ends, the data should go, unless a law requires it to stay.
Worked problem
Setting a retention period
A Canadian company keeps sales invoices supporting its tax returns. The tax year ends 31 December 2025 and the return is filed in June 2026. No objection or appeal is under way. Its policy adds one year to legal minimums. When can the invoices for 2025 be destroyed?
Show solution
- Legal minimum: six years from the end of the last tax year to which the records relate.
- End of the 2025 tax year: 31 December 2025, so the minimum runs to 31 December 2031.
- Policy margin of one year: keep to 31 December 2032.
- Destroy in early 2033, after confirming no audit, objection or legal hold applies.
Answer: Early 2033, subject to checking for audits, objections and legal holds.
Legal holds
A legal hold, also called a litigation hold or preservation order, suspends normal disposal for records relevant to actual or reasonably anticipated litigation, investigations or audits. Once the organization reasonably expects a dispute, it has a duty to preserve relevant information, and destroying it, even under the normal retention schedule, can lead to court sanctions and adverse inferences. Legal holds are issued by legal counsel, identify the custodians and data sources involved, override retention rules for the affected records, and remain in place until counsel formally releases them.
Security and IT teams play a key role. They must be able to suspend automatic deletion for particular mailboxes, accounts, devices and cloud repositories; preserve departing employees' data and devices when holds apply; and track which systems are under hold. Many email and collaboration platforms have built-in hold features that preserve content without users knowing, which avoids tipping off a custodian who might delete evidence. Holds should be reviewed regularly, because forgotten holds become over-retention.
Records management
Records management is the discipline of managing records, meaning information created or received as evidence of business activities, throughout their life. ISO 15489-1:2016 sets out international principles. Records management decides what counts as a record, classifies records into the categories of the retention schedule, makes sure records are authentic, reliable, complete and usable, and carries out disposition. Not everything is a record: drafts, convenience copies and transitory messages often are not, and policies should say so, so that they can be deleted promptly.
Federal government institutions in Canada are subject to the Library and Archives of Canada Act, under which government records may not be destroyed without the authorization of the Librarian and Archivist of Canada, usually through approved disposition authorities, and records of archival value are transferred to Library and Archives Canada. Provinces have similar archives and records laws for public bodies. Access to information laws, such as the federal Access to Information Act, make it an offence to destroy records to prevent their disclosure in response to a request.
Electronic records raise specific challenges. Email and chat contain records mixed with trivia; cloud services keep versions and deleted items; and records may need to stay readable and authentic for decades. Records management systems can enforce retention automatically: labels applied to records trigger retention and disposition when the trigger event occurs, and disposition can require review by an owner before destruction.
Making disposal happen
Most organizations are better at keeping data than at getting rid of it. Disposal fails because no one owns it, because people fear deleting something they might need, and because data is spread across too many places. Practical steps include automating disposition in systems that support it, setting retention policies on email and collaboration platforms, scheduling periodic clean-ups of file shares and legacy systems with owner sign-off, and including disposal in system decommissioning plans. Backups need special thought: rather than editing backups to remove individual records, organizations usually let them expire on a defined cycle, keep backup retention as short as recovery needs allow, and prevent restored backups from bringing deleted records back into production.
Worked problem
The cost of over-retention
A retailer keeps 2.4 million records of former customers who have not purchased in more than five years, although its schedule calls for deletion after three years without activity. An attacker steals the database. Using an illustrative breach cost of $8 per record, what did over-retention add to the cost?
Show solution
- Records that should already have been deleted: 2.4 million.
- Added cost at $8 per record: 2,400,000 × $8 = $19,200,000.
- Additional harms: more affected people to notify, more regulatory exposure, and reputational damage among former customers.
Answer: About $19.2 million in additional cost on these illustrative assumptions, plus regulatory and reputational harm, for records with no remaining business value.
Thinking like a manager
Exam questions on retention often ask what overrides what. A legal hold overrides the normal schedule; the schedule overrides individual preferences; legal minimums set the floor and privacy principles set the ceiling. The right answer to an employee who wants to keep everything forever is the schedule, and the right answer to a request to delete records relevant to anticipated litigation is to refer it to legal counsel and preserve them. Retention decisions belong to owners, guided by legal counsel and records managers, and carried out by custodians.
Retention in email and collaboration platforms
Email, chat and collaboration platforms deserve their own retention rules, because they hold a mixture of records, transitory messages and personal information, and because users rarely sort them. Common approaches set a default retention period for mailboxes and chats, such as two or three years, apply longer labels to messages that are records, and delete everything else automatically when its period ends. Chat messages are increasingly treated like email for discovery purposes, so courts and regulators expect them to be covered by the schedule and by legal holds. Personal messaging apps used for business, such as text messages on personal phones, are a growing problem: regulators in the financial sector have fined firms heavily for failing to retain business communications sent through unapproved apps. The simplest control is to provide approved tools with built-in retention and to prohibit business use of unapproved ones.
Common mistakes
MistakeKeeping everything forever in case it is needed.
InsteadOver-retention increases breach, privacy and discovery costs; follow the schedule.
MistakeDestroying records under the normal schedule after litigation is anticipated.
InsteadA legal hold overrides the schedule; preserve and refer to counsel.
MistakeSetting retention periods without citing their legal basis.
InsteadRecord the source of each period so it can be checked and updated.
MistakeApplying the schedule only to official file systems.
InsteadInclude email, chat, cloud services, devices and backups.
MistakeLeaving legal holds in place after cases end.
InsteadReview holds and release them formally when counsel agrees.
Summary and key terms
- Retention balances legal minimums against privacy maximums and the risks of keeping data too long.
- A retention schedule lists categories, trigger events, periods, legal basis, owner and disposition.
- In Canada, tax records are generally kept six years from the end of the relevant tax year; PIPEDA requires keeping personal information only as long as necessary.
- Legal holds suspend normal disposal for records relevant to litigation or investigations until counsel releases them.
- Records management ensures records are authentic, reliable and disposed of according to approved authority.
- Disposal needs owners, automation and attention to backups and legacy systems.
- Over-retention multiplies the cost and harm of breaches.
- Retention schedule
- A list of record categories with retention periods, triggers, basis and disposition.
- Trigger event
- The event that starts a retention period, such as contract end.
- Disposition
- What happens at the end of retention: destruction, transfer or review.
- Legal hold
- A suspension of disposal for records relevant to litigation or investigation.
- Spoliation
- Destruction or alteration of evidence relevant to legal proceedings.
- Electronic discovery
- The identification and production of electronic records in legal proceedings.
- Record
- Information created or received as evidence of business activity.
- Transitory record
- Information of short-term value that is not an official record.
- Storage limitation
- The GDPR principle of keeping personal data no longer than necessary.
- WORM storage
- Write once, read many storage that prevents alteration.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name two harms of over-retention.
Show answer
Larger breaches, higher discovery costs, harder access requests and privacy violations.
What does a retention schedule record for each category?
Show answer
Trigger, period, legal basis, owner and disposition.
How long does the Income Tax Act generally require business records to be kept?
Show answer
Six years from the end of the last tax year to which they relate.
What does PIPEDA require when personal information is no longer needed?
Show answer
Destroy, erase or anonymize it.
What overrides the normal retention schedule?
Show answer
A legal hold.
Who issues and releases legal holds?
Show answer
Legal counsel.
Which international standard covers records management principles?
Show answer
ISO 15489-1:2016.
Why are transitory records important to define?
Show answer
So they can be deleted promptly rather than retained as records.
How are individual records usually removed from backups?
Show answer
Backups expire on a defined cycle, and restored backups are prevented from reintroducing deleted records.
Who decides retention for a data set?
Show answer
The owner, guided by legal counsel and records management.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.