
CISSP-116 · Lesson 2 of 12 · 30 min
Investigations and evidence
Sooner or later every security team has to find out what happened and prove it. An employee may be suspected of copying customer lists before resigning. A regulator may ask how personal information came to be exposed. Police may request records about a fraud that passed through the company's systems. A customer may sue over a service failure. In each case the organization needs an investigation that is lawful, fair and thorough, and evidence that will stand up to scrutiny by managers, auditors, regulators and possibly a court.
Sub-domain 7.1 of the CISSP outline, understand and comply with investigations, expects a manager's command of investigation types, evidence handling, the main legal rules about admissibility and the practical steps that keep an investigation defensible. It does not expect you to perform technical forensics. This lesson keeps to that level: what investigators must preserve and document, who should be involved, and how the law in Canada and the United States shapes the process. Specialist digital forensic work is done by trained examiners using validated tools, under the governance described here.
Types of investigation
The type of investigation determines its purpose, who leads it, the standard of proof and what the organization may do with the results. Confusing the types is a common and costly mistake, because an investigation that starts as an internal HR matter can turn into a criminal case, and evidence handled casually at the start may be unusable later.
| Type | Purpose | Typical lead | Standard of proof |
|---|---|---|---|
| Administrative (internal) | Resolve a policy or operational issue; support HR action | Security, HR, internal audit | Organizational policy; fairness and reasonableness |
| Civil | Resolve a dispute between parties, often for damages | Legal counsel, with experts | Balance of probabilities (Canada); preponderance of the evidence (US) |
| Criminal | Determine whether a crime was committed and prosecute | Police and prosecutors | Beyond a reasonable doubt |
| Regulatory | Determine compliance with a law or regulation | Regulator, with the organization's cooperation | Set by the statute; often balance of probabilities |
| Industry standard | Determine compliance with a contractual standard such as PCI DSS | Qualified assessor or forensic investigator | Set by the standard and contract |
Because any internal investigation might later become civil, criminal or regulatory, the safest practice is to handle evidence from the first day as if it may end up in court. That does not mean every HR matter needs a forensic laboratory, but it does mean preserving original data, documenting who did what and when, and involving legal counsel early when the stakes are high. In both countries, involving counsel early can also bring the investigation under solicitor-client (Canada) or attorney-client (US) privilege and litigation privilege or work-product protection, which can keep sensitive analysis confidential. Privilege depends on facts and must be planned with counsel, not assumed.
What makes evidence useful
Evidence is any information that tends to prove or disprove a fact in issue. Investigators describe evidence by its form and its relationship to the facts. Real evidence is a physical object, such as a laptop or a USB drive. Documentary evidence includes records, emails, logs and contracts. Testimonial evidence is what witnesses say. Direct evidence proves a fact without inference, such as a witness who saw an employee remove a server; circumstantial evidence requires inference, such as logs showing the employee's badge entered the server room just before the server went offline.
For evidence to be useful in any forum it should be relevant (related to a fact in issue), reliable (accurate and produced by a trustworthy process), complete (not selectively extracted) and authentic (shown to be what it claims to be). Digital evidence raises special concerns: it is easy to alter without trace, it can be changed simply by examining it carelessly, and much of it is produced automatically by systems whose reliability must itself be shown.
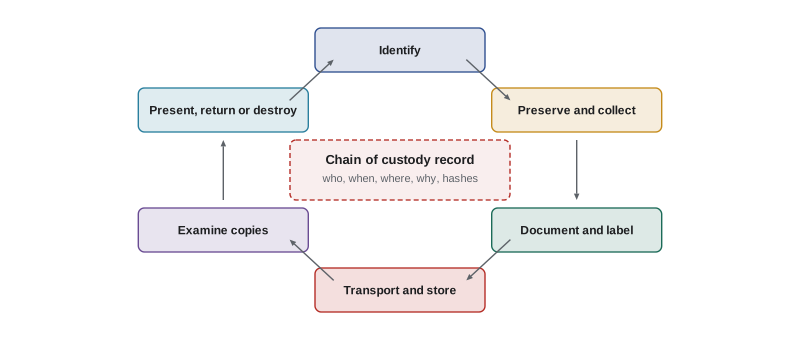
Chain of custody
The chain of custody is the documented, unbroken record of who has had possession of an item of evidence, from the moment it was collected until it is presented or disposed of, together with what was done to it and why. Its purpose is to show that the evidence presented is the same evidence that was collected and that it has not been altered, substituted or contaminated. A gap in the chain does not automatically make evidence worthless, but it invites challenge and reduces the weight a decision-maker gives it.
A good custody record captures, for each item: a unique identifier; a description, including make, model and serial number for devices; where, when and by whom it was found and collected; each transfer, with date, time, the people releasing and receiving it, and the purpose; storage location and conditions; and for digital evidence, the cryptographic hash values computed at collection and at each later verification. Evidence is sealed in tamper-evident bags or containers, stored in a locked area with access logs, and handled by as few people as possible.
import hashlib, json
# Integrity check of a preserved evidence file against the value recorded at collection
evidence = b'2026-09-14T02:11:08Z host=fin-db01 user=svc_backup action=export rows=48211\n' * 3
collected_hash = hashlib.sha256(evidence).hexdigest()
log = [
    {'when': '2026-09-14 09:05', 'from': 'J. Park (collector)', 'to': 'Evidence locker 2', 'purpose': 'Initial storage'},
    {'when': '2026-09-15 13:20', 'from': 'Evidence locker 2', 'to': 'R. Diaz (examiner)', 'purpose': 'Create working copy'},
    {'when': '2026-09-15 16:45', 'from': 'R. Diaz (examiner)', 'to': 'Evidence locker 2', 'purpose': 'Return original'},
]
later_copy = bytes(evidence)
print('Collected SHA-256 :', collected_hash[:32], '...')
print('Verified SHA-256  :', hashlib.sha256(later_copy).hexdigest()[:32], '...')
print('Integrity verified:', hashlib.sha256(later_copy).hexdigest() == collected_hash)
print('Custody transfers recorded:', len(log))
for e in log:
print(f" {e['when']} {e['from']} -> {e['to']} ({e['purpose']})")Collected SHA-256 : 85020e10996b83e540133a529cfcffc7 ... Verified SHA-256 : 85020e10996b83e540133a529cfcffc7 ... Integrity verified: True Custody transfers recorded: 3 2026-09-14 09:05 J. Park (collector) -> Evidence locker 2 (Initial storage) 2026-09-15 13:20 Evidence locker 2 -> R. Diaz (examiner) (Create working copy) 2026-09-15 16:45 R. Diaz (examiner) -> Evidence locker 2 (Return original)
Hash values are the digital equivalent of a tamper-evident seal. If the hash of a preserved image matches the value recorded at collection, any change, even of a single bit, would have produced a different value. Examiners analyse verified working copies, never the original, so the original can be re-examined by another expert if the findings are challenged.
Order of volatility and collection priorities
Some digital evidence disappears quickly. The contents of memory vanish when a system is powered off; network connections and running processes change by the second; temporary files are overwritten; logs roll over on schedule; while data on disks and backups persists far longer. The order of volatility is the principle that collection should generally begin with the most volatile sources and move to the most persistent. RFC 3227, a long-standing guideline on evidence collection, describes this ordering.
Order of volatility is a planning concept, not a recipe, and it must be balanced against other priorities. Pulling the plug on a server preserves the disk but destroys memory; leaving it running preserves memory but lets an intruder, or an automatic process, keep changing data. Business needs matter too: shutting down a payment system has costs. These decisions should be made by people with the authority and skill to make them, following a pre-approved procedure, and recorded with the reasons. For managers, the key point is that responders should be trained and equipped before an incident, because improvised collection is where evidence is most often lost.
| Source (most to least volatile) | Why it is fragile | Management decision it raises |
|---|---|---|
| System memory and running state | Lost at power-off; changes constantly | Whether to keep the system running for capture |
| Network state and active connections | Changes second by second | Whether to isolate rather than unplug |
| Temporary files and caches | Overwritten by normal activity | How quickly to preserve |
| Logs on the system | Rotated or overwritten on schedule | Whether central log retention already covers it |
| Disk contents | Persistent but alterable | Whether to image now or after containment |
| Backups and archives | Most persistent | Whether to place a legal hold on rotation |
Legal holds and e-discovery
When litigation or a regulatory investigation is reasonably anticipated, the organization has a duty to preserve relevant information. A legal hold (litigation hold) is the instruction, usually issued by legal counsel, that suspends normal deletion and rotation for specified records and systems. Security and IT operations implement it: pausing automatic deletion, preserving mailboxes of departing custodians and keeping backups that would otherwise be overwritten. Failing to preserve can lead to court sanctions or adverse inferences, so legal holds must be tracked, communicated to custodians and released formally when the matter ends.
Electronic discovery (e-discovery) is the process of identifying, preserving, collecting, reviewing and producing electronically stored information in litigation. In the United States, the Federal Rules of Civil Procedure set detailed expectations, and many practitioners use the Electronic Discovery Reference Model to describe the stages. In Canada, the Sedona Canada Principles are widely referenced by courts and practitioners, alongside provincial rules of civil procedure. Good records management, including a retention schedule and knowing where data lives, makes discovery far cheaper and less risky.
Admissibility: the law in your country
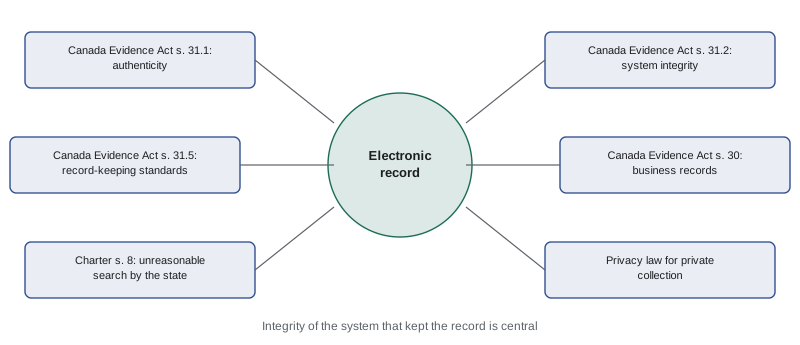
In Canada, the admissibility of electronic documents is addressed by the Canada Evidence Act, sections 31.1 to 31.8, and by similar provisions in provincial evidence acts. The party relying on an electronic document must prove its authenticity, meaning evidence capable of supporting a finding that it is what it is claimed to be. The best evidence rule for electronic documents is satisfied by proof of the integrity of the electronic documents system that recorded or stored it, and integrity can be presumed from evidence that the system was operating properly, or by evidence that the record was stored by a party adverse in interest, or in the usual and ordinary course of business. Section 31.5 lets courts consider standards, procedures and practices for record-keeping, which is why documented logging and records management practices strengthen evidence. Business records are also admissible under section 30, subject to its conditions. Search and seizure by the state is governed by section 8 of the Charter of Rights and Freedoms, which protects against unreasonable search and seizure; private organizations collecting evidence must also respect privacy law, including PIPEDA or substantially similar provincial laws, and employment law on monitoring. Ontario, for example, requires employers with 25 or more employees to have a written electronic monitoring policy.
Running an internal investigation fairly
Many investigations never reach a court, but they still affect people's livelihoods and reputations, and they can be reviewed later by tribunals, arbitrators or courts. A defensible internal investigation has a clear mandate and scope approved by an appropriate executive, an investigator who is independent of the matter and competent, a plan that considers legal privilege, privacy and employment law, interviews conducted fairly with notes kept, and conclusions that follow from the evidence. The person under investigation should normally have a chance to respond before conclusions are reached. Monitoring of employees must comply with the organization's own notices and policies; evidence gathered by monitoring that employees were never told about, or that goes beyond what policy allows, may be challenged.
Worked problem
Handling a departing employee suspected of taking customer data
A sales manager resigns to join a competitor. A colleague reports that the manager downloaded the full customer list two days before resigning. HR wants to search the manager's laptop immediately.
Show solution
- Stop and involve legal counsel, because the matter may become civil litigation and privilege should be considered.
- Issue a legal hold covering the manager's mailbox, file shares, laptop and relevant logs, and suspend the deletion that normally follows a departure.
- Collect the laptop when it is returned, seal and label it, record the chain of custody and have a trained examiner create a verified forensic image.
- Preserve central evidence that does not depend on the laptop: data loss prevention alerts, cloud storage audit logs and email logs, with hashes recorded.
- Confirm that the acceptable use and monitoring policies the manager acknowledged permit this review.
- Analyse working copies only, document findings factually, and give counsel a report that separates facts from opinions.
Answer: Preserve first under legal guidance, keep a clean chain of custody, rely on central logs as well as the device, and stay within the monitoring policy.
Worked problem
When to call the police
An internal review finds strong signs that an outsider used stolen credentials to divert supplier payments worth $240,000.
Show solution
- Recognize that this is likely criminal fraud and that recovery of funds may depend on speed: contact the bank immediately.
- Consult legal counsel and senior management about reporting to police, cyber insurers and, where applicable, regulators.
- Report to law enforcement through the appropriate channel, and preserve evidence in a way that supports a criminal standard of proof.
- Understand that once police are involved, they may direct some evidence handling, and the organization should avoid actions that could compromise their case.
Answer: Treat it as a likely criminal matter from the start: act quickly with the bank, involve counsel, report to police and preserve evidence to the criminal standard.
Common mistakes
MistakeExamining the original device directly to save time.
InsteadCreate a verified copy and analyse the copy, keeping the original sealed.
MistakeStarting an internal investigation without considering that it may become criminal or civil.
InsteadHandle evidence from the outset as if it may go to court, and involve counsel early.
MistakeLetting normal deletion continue after litigation is anticipated.
InsteadIssue and enforce a legal hold on relevant systems and records.
MistakeLeaving gaps in the chain of custody record.
InsteadRecord every transfer, purpose, location and verification hash.
MistakeMonitoring employees beyond what policy and law allow.
InsteadInvestigate within notified monitoring policies and privacy and employment law.
MistakePowering off every system immediately as a rule.
InsteadFollow a pre-approved procedure that weighs volatile evidence, containment and business impact.
Summary and key terms
- Investigations may be administrative, civil, criminal, regulatory or industry-standard, each with a different purpose and standard of proof.
- Because internal matters can escalate, evidence should be handled from the start as if it may go to court.
- Useful evidence is relevant, reliable, complete and authentic.
- The chain of custody records every handler, transfer, purpose and hash so that evidence can be shown to be unaltered.
- The order of volatility guides collection priorities but must be balanced against containment and business impact.
- Legal holds suspend deletion when litigation or regulatory action is anticipated.
- Admissibility rules differ: Canada stresses authenticity and system integrity; the US uses authentication, hearsay exceptions and the best evidence rule.
- Chain of custody
- The documented record of possession and handling of evidence from collection to disposal.
- Order of volatility
- The principle of collecting the most short-lived evidence first.
- Legal hold
- An instruction suspending deletion of records relevant to anticipated litigation or investigation.
- E-discovery
- Identifying, preserving, collecting, reviewing and producing electronically stored information.
- Hash value
- A fixed-length digest that changes if the underlying data changes, used to verify integrity.
- Real evidence
- A physical object offered as evidence.
- Circumstantial evidence
- Evidence that proves a fact by inference.
- Authentication
- Showing that evidence is what its proponent claims it to be.
- Business records exception
- A rule admitting regularly kept business records despite the hearsay rule.
- Litigation privilege
- Protection of materials prepared for the dominant purpose of litigation.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What standard of proof applies in a criminal case?
Show answer
Beyond a reasonable doubt.
Why should internal investigations handle evidence as if it may go to court?
Show answer
Because internal matters can become civil, criminal or regulatory, and poorly handled evidence may be unusable later.
Name four qualities of useful evidence.
Show answer
Relevant, reliable, complete and authentic.
What does a chain of custody record contain?
Show answer
Identifier, description, collection details, every transfer with dates, people and purpose, storage location and hash verifications.
Why do examiners work on copies?
Show answer
To avoid altering the original, which can then be re-examined if findings are challenged.
Which is generally more volatile: system memory or backups?
Show answer
System memory.
What is a legal hold and who usually issues it?
Show answer
An instruction to suspend deletion of relevant records, usually issued by legal counsel.
Which Canadian statute addresses electronic documents as evidence?
Show answer
The Canada Evidence Act, sections 31.1 to 31.8.
Which US rule provides the business records exception?
Show answer
Federal Rule of Evidence 803(6).
Why should the investigated person normally be allowed to respond before conclusions?
Show answer
Fairness, and because internal findings may be reviewed later by tribunals, arbitrators or courts.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.