
SLS-150 · Lesson 8 of 12 · 18 min
Customer data and privacy under PIPEDA
▶ Video coming soon A video version of this lesson is on the way.
On a Saturday evening in early November, Aiden left Juniper & Pine's sales tablet on the seat of a bus. It held the store's delivery app, which showed names, addresses, phone numbers and delivery notes for the 37 customers whose orders were scheduled for the following week. He realized what had happened on the walk home, called the transit lost-and-found, then called Bev. Bev's first questions were practical: Was the tablet locked? Was it encrypted? Could the store wipe it remotely? The answers were yes, yes and yes. Marcus Dube wiped it within the hour. But the store still had to work out whether it had a privacy breach on its hands, and what the law required it to do next.
Selling runs on information about people: names, job titles, contact details, purchase histories, preferences, notes from conversations and, increasingly, data from websites and apps. Privacy law governs how businesses collect, use, share and protect that information. Sellers handle personal information every day, often more of it than anyone else in the company, so they are on the front line of privacy compliance. This lesson explains the privacy law that applies in your country, what it means for CRM records and sales conversations, and what to do when something goes wrong.
PIPEDA and who it covers
The Personal Information Protection and Electronic Documents Act, known as PIPEDA, is the federal law governing how private-sector organizations collect, use and disclose personal information in the course of commercial activities. It applies in Saskatchewan, which, unlike Alberta, British Columbia and Quebec, has no provincial private-sector privacy law of its own. Personal information means information about an identifiable individual, which includes a customer's name, home address, purchase history and the notes a seller writes about them. Business contact information, such as a person's name, title and work email, is excluded when it is used solely to communicate with them about their job, but it is still personal information if it is used for something else, such as building a marketing profile. Health information held by trustees such as clinics in Saskatchewan is also governed by The Health Information Protection Act, which matters when Ridgeline handles data for clinic customers like Northfield.
The ten fair information principles
PIPEDA is built on ten fair information principles, set out in a schedule to the Act. Organizations must be accountable for the information they hold, identify the purposes for collecting it before or at the time of collection, obtain meaningful consent, limit collection to what is needed for those purposes, limit use, disclosure and retention to those purposes, keep information accurate, protect it with safeguards suited to its sensitivity, be open about their practices, give individuals access to their own information, and let individuals challenge compliance. The Office of the Privacy Commissioner of Canada oversees PIPEDA, investigates complaints and publishes guidance, but under the current law it cannot impose fines for most violations; the Federal Court can award damages after a complaint, and fines of up to 100,000 dollars apply to specific offences, such as knowingly failing to report a breach.
| Principle | In practice for a seller |
|---|---|
| Purpose | Know why you are collecting each piece of information, and tell the customer |
| Consent | Get agreement for anything a customer would not reasonably expect, such as adding them to a newsletter |
| Limit collection | Record what you need to serve the customer, not everything you hear |
| Limit use and disclosure | Use data for the purpose given; do not pass it to partners without a basis |
| Accuracy | Update contact records when they change |
| Safeguards | Lock devices, use approved systems and never keep customer lists on personal accounts |
| Access | Know how to route a customer's request to see or correct their information |
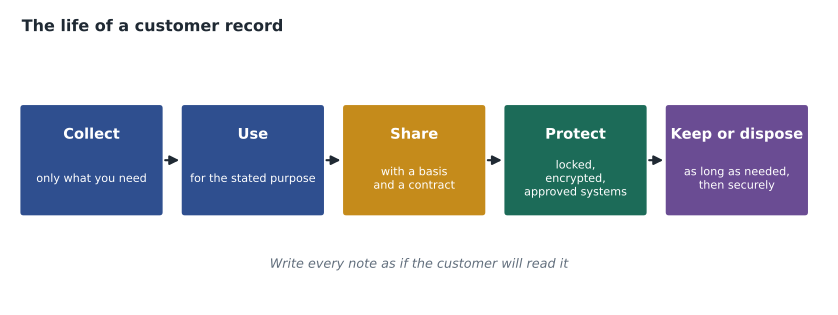
What goes in the CRM notes
The CRM is the biggest store of personal information most sales teams have, and sellers write most of what is in it. Darnell's rule for Ridgeline is that CRM notes should be written as if the customer will read them, because under the law customers can often ask to see them. Write facts and business needs. Do not record health details, family circumstances, personal opinions about the buyer or gossip unless there is a clear business reason and the customer would expect it.
| Better | Worse |
|---|---|
| "Office manager prefers email; back from leave Nov 2." | "Janet was off with a back injury, seemed stressed." |
| "Decision needs Dr. Anand's approval above 5,000." | "Dr. Anand is difficult and cheap." |
| "Clinic expanding into the unit next door in January." | "Heard from the landlord their lease is in trouble." |
| "Asked us not to call before 10 a.m." | "Grumpy in the mornings." |
Sharing data with partners and service providers
Juniper & Pine shares some customer information with its financing partner when a customer applies for credit, with its delivery contractor and with the company that administers protection plans. Under PIPEDA, the store remains accountable for personal information it transfers to a service provider for processing, and must use contracts and other means to make sure the provider protects it to a comparable level. Sharing for a new purpose, such as letting the lender market its own products to Juniper & Pine's customers, needs the customer's consent. For Ridgeline, service work for clinics is more sensitive: when its technicians service a multifunction printer at Northfield, the device's memory may hold scanned patient records. Ridgeline's contract with the clinic requires the hard drive to be wiped or kept on site when a machine is removed, which supports the clinic's own obligations under The Health Information Protection Act.
When something goes wrong: breaches
PIPEDA requires an organization to report a breach of security safeguards involving personal information to the Privacy Commissioner, and to notify affected individuals, if it is reasonable to believe the breach creates a real risk of significant harm. Significant harm includes humiliation, damage to reputation or relationships, financial loss, identity theft and similar harms. Whether a risk is real depends mainly on the sensitivity of the information and the probability that it has been, is being or will be misused. Organizations must give notice as soon as feasible. They must also keep a record of every breach of security safeguards, whether or not it is reportable, for 24 months, and give it to the Commissioner on request.
Worked problem
Assessing the lost tablet
Aiden's tablet held names, addresses, phone numbers and delivery notes for 37 customers. It was locked with a passcode, its storage was encrypted, and it was wiped remotely about an hour after it was lost. Does Juniper & Pine need to report or notify?
Show solution
- Identify the information: contact details and delivery notes. No payment card numbers, government ID numbers or account numbers were on the device.
- Consider the safeguards: the device was encrypted, locked and wiped, so the chance anyone accessed the data is very low.
- Apply the test: given moderately sensitive information and a very low probability of misuse, there is likely no real risk of significant harm, so a report to the Commissioner and notices to customers are probably not required.
- Record it anyway: the store must keep a record of the breach for 24 months, including the facts, the assessment and the steps taken.
- Consider customers as people: Bev decided to call the customers with deliveries that week to explain, confirm their delivery times and answer questions.
Answer: The store probably did not have a reportable breach, because of the encryption and remote wipe, but it documented the incident and told the customers anyway. If the tablet had been unlocked and unencrypted, the answer could have been different.
Reform: Bill C-36
Privacy law in Canada is changing. Bill C-27, which would have replaced the privacy part of PIPEDA with a new Consumer Privacy Protection Act, died when Parliament was prorogued in January 2025. In June 2026, the government introduced Bill C-36, the proposed Protecting Privacy and Consumer Data Act. As introduced, it would replace Part 1 of PIPEDA, describe privacy as a fundamental right, move oversight to a new Digital Safety and Data Protection Commission with a Privacy and Consumer Data Commissioner who could issue orders and impose administrative penalties of up to the greater of 10 million dollars and 3 per cent of global revenue, add stronger protection for children's information, and let individuals sue after a contravention has been established. It would also name "inappropriate surveillance pricing", meaning using personal information to set individual prices unfairly, as an unfair use. As of November 2026, the bill had only passed first reading, so PIPEDA remains the law. Sellers should expect stronger enforcement in the coming years and watch for their company's updated policies.
Access requests and AI tools
Customers have a right to see the personal information an organization holds about them. Under PIPEDA, an organization must generally respond to a written access request within 30 days, provide the information at minimal or no cost, and correct information shown to be inaccurate. A seller who receives such a request should not try to answer it alone, but should pass it immediately to the person responsible for privacy, usually named in the company's privacy policy. Because CRM notes can be included, the habit of writing notes as if the customer will read them has a practical purpose.
A newer risk comes from AI tools. It is tempting to paste a customer's email thread or a list of contacts into a public AI chatbot to draft a reply or summarize a meeting. Doing so may disclose personal and confidential information to a third party, outside the company's control and possibly outside the country. Ridgeline allows only the AI assistant built into its CRM, which the company has assessed and contracted for, and prohibits pasting customer information into other tools. The same caution applies to recording meetings with transcription tools: the other participants should know, and the recordings belong in approved systems.
| Habit | Why it matters |
|---|---|
| Lock your laptop and phone whenever you step away | Most breaches start with simple lapses |
| Use only approved systems for customer data | Personal email and cloud accounts are outside the company's safeguards |
| Do not paste customer data into public AI tools | It discloses data to a third party |
| Shred printed customer documents | Paper is still a common source of breaches |
| Report lost devices and misdirected emails at once | Fast reporting limits harm and is often legally required |
Retention: how long to keep customer data
Privacy law in both countries expects organizations to keep personal information only as long as it is needed. Some records must be kept for set periods, such as invoices and tax records, and some contracts specify retention. Beyond those, keeping old prospect lists, closed opportunity notes and former customers' details indefinitely increases the harm if a breach happens and makes access requests harder to answer. Ridgeline's CRM now flags prospect records with no activity for three years for review, and the sales team either refreshes consent or deletes them. Juniper & Pine deletes delivery notes, such as gate codes and parking instructions, ninety days after delivery, because they are useful for the delivery and risky afterwards.
Privacy questions also come up in ordinary selling conversations. A clinic manager may ask whether a technician will see patient files on a printer's screen during a repair, or a customer may ask why the store needs a phone number for a delivery. Short, accurate answers, such as explaining that the number is used only to arrange the delivery and is deleted afterwards, build trust and show that the business takes privacy seriously.
Common mistakes
MistakeCustomer data belongs to the seller who collected it.
InsteadIt belongs in the company's systems, and the company is accountable for it. Never take customer lists to a personal account or a new employer.
MistakeAnything a customer tells me can go in the CRM.
InsteadRecord what you need for the business relationship, written as if the customer will read it.
MistakeIf a device is lost, we only need to act if we know someone accessed the data.
InsteadAssess the risk based on the data and safeguards, document the incident and follow the notification rules.
MistakePassing customer details to a partner is fine if it helps the customer.
InsteadSharing for a new purpose needs a legal basis, often the customer's consent, and service providers need contracts.
MistakePrivacy is the IT department's job.
InsteadSellers handle more personal information than almost anyone and are part of compliance.
Summary and key terms
- PIPEDA governs private-sector handling of personal information in Saskatchewan; health information held by trustees is also covered by The Health Information Protection Act.
- PIPEDA's ten principles require purpose, meaningful consent, limited collection, use and retention, accuracy, safeguards, openness and access.
- CRM notes should record business facts, written as if the customer will read them.
- Breaches creating a real risk of significant harm must be reported and notified, and every breach must be recorded for 24 months.
- Bill C-36, introduced in June 2026, would replace PIPEDA with a new act and stronger penalties, but is not yet law.
- Personal information
- Information about an identifiable individual.
- Meaningful consent
- Consent given by someone who understands what will be collected, why and with whom it will be shared.
- Real risk of significant harm
- The test for when a breach must be reported to the Privacy Commissioner and individuals notified.
- Service provider
- An organization that processes personal information on another organization's behalf.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Rewrite this CRM note: "Seemed stressed, said her mother is sick."
Show answer
Something like: "Asked us to follow up next week instead of this week."
Why did the encryption of the tablet matter?
Show answer
It made it very unlikely anyone could access the data, which affects whether the incident is a reportable breach.
Is Bill C-36 in force?
Show answer
No. As of November 2026 it had only passed first reading, so PIPEDA still applies.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.