
CISSP-111 · Lesson 11 of 12 · 27 min
Data security controls and compliance
Sub-domain 2.6 of the 2024 outline asks you to determine data security controls and compliance requirements. Lesson 7 covered the data states and protection methods. This lesson covers the rest of the sub-domain: how organizations choose control baselines, how they scope and tailor them to fit, how they select standards, and the three data protection technologies the outline names, digital rights management (DRM), data loss prevention (DLP) and cloud access security brokers (CASB). It also looks at compliance: how to show that the controls meet legal, regulatory and contractual requirements.
Baselines
A baseline is a minimum set of security controls for a category of system or data. Baselines save organizations from designing controls from scratch for every system and make protection consistent. They come from frameworks, standards and regulations: the NIST SP 800-53 low, moderate and high baselines, with SP 800-53B describing how they are built; the CIS Critical Security Controls implementation groups; ISO/IEC 27001 Annex A controls applied through a statement of applicability; PCI DSS for payment card environments; and sector or government profiles. Technical configuration baselines, such as CIS Benchmarks, apply the same idea to individual products, as lesson 5 described.
US federal systems are categorized under FIPS 199 and receive the NIST SP 800-53 baseline matching their high-water mark under FIPS 200; cloud services used by agencies are assessed under FedRAMP, which uses the same control families. Defense contractors handling CUI implement NIST SP 800-171, verified under the CMMC program. Many private organizations adopt NIST, ISO 27001 or CIS baselines, often alongside sector requirements such as HIPAA's Security Rule, the FTC Safeguards Rule for financial institutions and New York's 23 NYCRR 500 for regulated financial services companies.
Scoping and tailoring
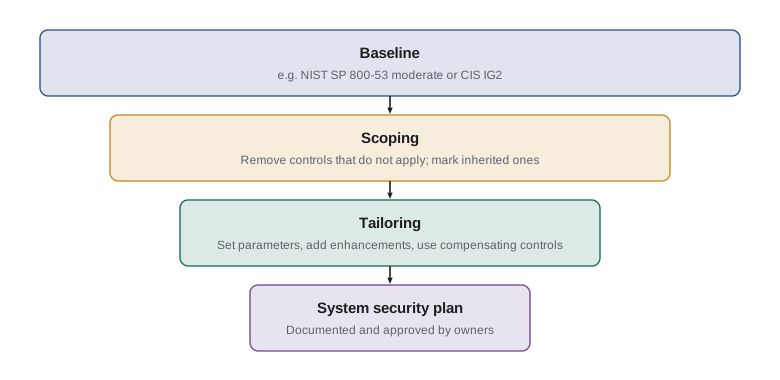
Baselines are starting points, not finished designs. Scoping is the process of determining which baseline controls apply to a particular system, by considering its technology, environment and data. A system with no wireless capability does not need wireless controls; a system hosted entirely by a software-as-a-service provider may inherit physical and environmental controls from the provider. Tailoring adjusts the scoped controls to the organization's specific risks and mission: strengthening some with control enhancements, adding supplemental controls, setting parameter values such as password length or log retention, and replacing controls that cannot be applied with compensating controls.
Tailoring decisions must be justified and documented, usually in a system security plan or statement of applicability, and approved by the system and data owners. Removing a control because it is inconvenient is not tailoring; removing it because the risk does not exist, or because a compensating control addresses the same risk, is. Common controls, provided once for many systems, such as a central logging service or an enterprise identity platform, can be inherited, with the inheriting system documenting the dependency.
Worked problem
Scoping and tailoring a baseline
A small analytics application processes confidential customer data. The organization applies a moderate baseline of about 280 controls and enhancements. The application runs on a cloud platform that provides 60 physical, environmental and infrastructure controls, which the application inherits. Another 25 controls cover technologies the application does not use. The data owner requires two additional controls: field-level encryption for one data element and quarterly access recertification. How many controls does the application team implement itself?
Show solution
- Start with the baseline: 280.
- Remove inherited controls, which are documented but implemented by the provider: 280 − 60 = 220.
- Remove controls scoped out because the technology is absent: 220 − 25 = 195.
- Add tailored supplemental controls: 195 + 2 = 197.
Answer: About 197 controls are implemented by the application team, with 60 inherited and 25 scoped out, all documented in the system security plan. The numbers are illustrative.
Selecting standards
The outline also asks you to select standards. Organizations choose which frameworks and standards to follow based on legal and regulatory requirements, contractual obligations, industry expectations, customer demands and their own risk appetite. A Canadian bank will follow OSFI guidelines; a US hospital must meet HIPAA; a retailer accepting cards must meet PCI DSS; a software company selling to enterprises will often pursue ISO 27001 certification or a SOC 2 report because customers ask for them. Many organizations use a unified control framework that maps one set of internal controls to several external standards, so a single control satisfies multiple requirements and evidence is collected once.
Standards selection should be driven by the business, not by fashion. Adopting a framework no customer or regulator requires may still be useful as a structure, but its cost should be justified by the assurance and risk reduction it brings.
Digital rights management
Digital rights management, often called information rights management (IRM) in enterprise settings, applies persistent protection to files so that controls travel with the information wherever it goes. A document protected with rights management is encrypted, and opening it requires authentication against a policy server that checks the user's permissions: view, edit, print, copy, forward, and for how long. Permissions can be revoked later, even after the file has left the organization, and access can be logged. Enterprise sensitivity labels often apply rights management automatically to confidential and restricted documents.
DRM has limitations. It requires compatible software on every device, can frustrate legitimate users and partners, and cannot stop someone photographing a screen or retyping content. It works best for high-value documents shared with a known set of people, such as board papers, merger documents and engineering drawings shared with suppliers. Consumer DRM, used to protect media such as films, music and e-books, follows similar principles and is protected in law against circumvention in both countries, under the Copyright Act in Canada and the Digital Millennium Copyright Act in the United States.
Data loss prevention
Data loss prevention tools discover, monitor and protect sensitive data to stop it leaving the organization inappropriately. Network DLP inspects traffic, such as email and web uploads, at the perimeter or in the cloud. Endpoint DLP runs on devices and controls actions such as copying to USB drives, printing, uploading through browsers and pasting into unapproved applications. Discovery DLP, sometimes called data-at-rest DLP, scans repositories to find sensitive data where it should not be. DLP identifies sensitive content using pattern matching (such as card number formats validated with the Luhn check), keywords, exact data matching against fingerprints of real records, document fingerprinting, machine learning classifiers and, most reliably, the sensitivity labels applied under the classification scheme.
DLP policies can monitor, warn, require justification, encrypt, quarantine or block. A typical rollout starts in monitoring mode to learn normal business flows, then introduces user warnings with justification, and only then blocks clearly prohibited actions. Tuning is critical: too many false positives and users ignore warnings or find workarounds, and analysts drown in alerts; too few rules and real leaks go unnoticed.
Worked problem
The false positive problem
An email DLP rule scans 200,000 outbound messages a month. Of these, 400 genuinely contain unprotected customer data. The rule catches 95 percent of genuine cases and wrongly flags 1 percent of the other messages. How many alerts are generated, and what share are real?
Show solution
- True positives: 95 % of 400 = 380.
- Messages without customer data: 200,000 − 400 = 199,600.
- False positives: 1 % of 199,600 = 1,996.
- Total alerts: 380 + 1,996 = 2,376.
- Share that are real: 380 ÷ 2,376 ≈ 16 percent.
Answer: About 2,376 alerts a month, of which only about 16 percent are real. Improving precision, for example by using classification labels and exact data matching, matters as much as catching every case.
Cloud access security brokers
A cloud access security broker (CASB) sits between users and cloud services to give visibility and control over cloud use. CASBs discover which cloud services employees use, including unsanctioned shadow IT, by analyzing network logs; rate the risk of each service; enforce policies on sanctioned services through application programming interface connections or inline proxies, such as blocking downloads of confidential files to unmanaged devices; apply DLP to cloud content; detect anomalous behavior such as mass downloads; and check cloud configurations. CASB capabilities are increasingly delivered as part of security service edge (SSE) or secure access service edge (SASE) platforms, which combine CASB with secure web gateways, zero trust network access and firewall services.
| Technology | Main question it answers | Where it acts | Typical limitation |
|---|---|---|---|
| DRM / IRM | Who can open and use this file, wherever it goes? | On the file, through a policy server | Needs compatible software; cannot stop screen photos |
| DLP | Is sensitive data leaving inappropriately? | Network, endpoint and repositories | False positives and tuning effort |
| CASB | Which cloud services are used, and how is data handled in them? | Between users and cloud services | Coverage gaps for unmanaged paths and new services |
Cloud data security and sovereignty
Data in the cloud needs the same controls as data on premises, applied through the provider's tools and the customer's configuration. Key practices include choosing regions deliberately and covering backups and support access in contracts; encrypting data with customer-managed keys for sensitive data; applying least-privilege identity and access management, which is the most common source of cloud breaches when misconfigured; enabling logging and monitoring; using cloud security posture management to detect misconfigurations such as public storage buckets; and planning exit, including data return and deletion. Data sovereignty concerns, discussed in lesson 6, may lead organizations to use providers or regions under domestic jurisdiction, or to hold their own keys so that the provider cannot be compelled to produce readable data.
Demonstrating compliance
Compliance means showing that controls meet requirements, not just having them. Evidence includes policies and standards, system security plans and statements of applicability, configuration records, access reviews, DLP and CASB reports, sanitization certificates, retention and disposal records, training records, and audit reports. Continuous control monitoring, which checks configurations and collects evidence automatically, reduces the effort and keeps evidence current. Independent assurance, such as ISO 27001 certification, SOC 2 Type II reports, PCI DSS reports on compliance and government assessments, gives customers and regulators confidence. Gaps found by audits feed back into the control set through a plan of action and milestones, tracked to closure by the owners.
Thinking like a manager
Exam questions in this area often ask which technology fits a need, or how to adapt a baseline. Persistent protection for a document after it leaves the organization points to DRM. Detecting or stopping sensitive data leaving points to DLP. Visibility and control over cloud services points to CASB. When a baseline control does not fit, the answer is scoping or tailoring with documented justification and compensating controls, approved by the owner, never silently dropping the control. And when choosing standards, follow legal, regulatory and contractual requirements first.
Common mistakes
MistakeApplying a baseline unchanged to every system.
InsteadScope and tailor the baseline to the system and document the decisions.
MistakeDropping inconvenient controls and calling it tailoring.
InsteadRemove controls only when the risk is absent or a compensating control addresses it, with owner approval.
MistakeTurning on DLP blocking rules on day one.
InsteadStart in monitoring mode, tune, warn, and then block clearly prohibited actions.
MistakeExpecting DRM to stop all leakage.
InsteadDRM protects files persistently but cannot stop screen photographs or retyping.
MistakeAssuming compliance follows from having controls.
InsteadCollect evidence and obtain independent assurance to demonstrate compliance.
Summary and key terms
- Baselines are minimum control sets from frameworks such as NIST SP 800-53, CIS Controls, ISO 27001 and PCI DSS.
- Scoping removes controls that do not apply and identifies inherited controls; tailoring adjusts controls to risk.
- Tailoring decisions must be justified, documented and approved by owners.
- Standards are selected mainly by legal, regulatory, contractual and customer requirements.
- DRM applies persistent, revocable protection to files; DLP detects and stops inappropriate data movement; CASB gives visibility and control over cloud use.
- DLP needs careful tuning because false positives can swamp real alerts.
- Compliance requires evidence and, often, independent assurance.
- Baseline
- A minimum set of security controls for a category of system or data.
- Scoping
- Determining which baseline controls apply to a particular system.
- Tailoring
- Adjusting scoped controls to specific risks, including parameters and supplemental controls.
- Common control
- A control provided once and inherited by many systems.
- Statement of applicability
- An ISO 27001 document listing which controls apply and why.
- Digital rights management
- Persistent, policy-based protection that travels with a file.
- Data loss prevention
- Tools that detect and prevent inappropriate movement of sensitive data.
- Exact data matching
- DLP detection that compares content against fingerprints of real records.
- Cloud access security broker
- A control point providing visibility and policy enforcement for cloud services.
- Cloud security posture management
- Tools that detect misconfigurations in cloud environments.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What is the difference between scoping and tailoring?
Show answer
Scoping decides which controls apply; tailoring adjusts them to risk.
Name two sources of control baselines.
Show answer
NIST SP 800-53, CIS Controls, ISO 27001 Annex A or PCI DSS.
What is a common control?
Show answer
A control provided once and inherited by many systems, such as central logging.
What drives standards selection first?
Show answer
Legal, regulatory and contractual requirements.
What can DRM do after a file leaves the organization?
Show answer
Enforce and revoke permissions and log access.
Name the three main types of DLP deployment.
Show answer
Network, endpoint and discovery.
Why start DLP in monitoring mode?
Show answer
To learn normal flows and tune rules before blocking.
How does a CASB discover shadow IT?
Show answer
By analyzing network logs for cloud service use.
What is the most common source of cloud data breaches?
Show answer
Customer misconfiguration, especially of identity and storage access.
Give two kinds of compliance evidence.
Show answer
Examples include access reviews, sanitization certificates, configuration records and audit reports.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.