
CISSP-111 · Lesson 2 of 12 · 25 min
Classification schemes and labeling in the US and in business
Classification is the process of deciding how sensitive or critical an asset is and placing it in a category that carries a defined set of protections. It is the bridge between knowing what you have, the subject of lesson 1, and knowing how to handle it, the subject of lesson 4. A good scheme lets thousands of people make consistent decisions without consulting the security team each time: if a document is marked confidential, everyone knows it must not be emailed outside the company unencrypted, left on a printer or posted in a public channel. This lesson covers why classification matters, how government and commercial schemes differ, how to choose the right number of levels, and how labeling and marking make classification visible.
Why classify
Without classification, organizations tend to fall into one of two failure modes. Either they protect everything at the highest level, which is expensive, slows work down and leads people to find workarounds, or they protect everything at a low level, which leaves the most sensitive information exposed. Classification lets protection be proportionate: strong controls where the harm from compromise is high, lighter controls where it is low. It also supports legal compliance, because many laws attach obligations to particular categories of data such as personal health information or payment card data, and it gives incident responders a quick way to judge how serious a loss is.
Classification normally considers the harm from compromise of each of the core properties. Confidentiality asks how much damage unauthorized disclosure would cause. Integrity asks how much damage unauthorized or accidental change would cause. Availability asks how much damage loss of access would cause, and for how long the organization could cope. Some schemes record a separate rating for each; others focus on confidentiality and handle availability through the business impact analysis. Either way, the classification decision should rest on harm, not on who created the information or how important the author feels.
Government classification
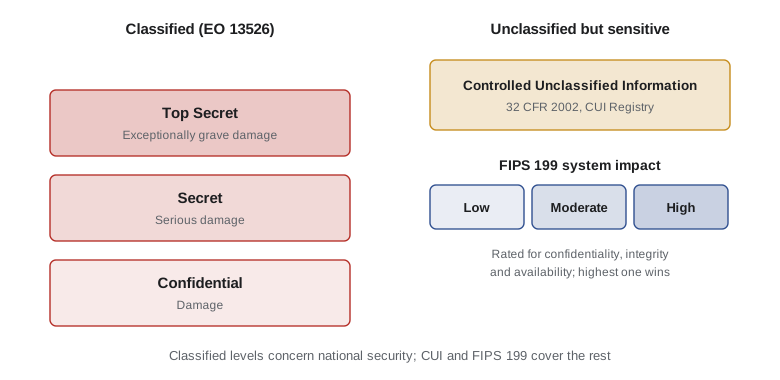
The US federal government classifies national security information under Executive Order 13526 (2009). There are three levels: Confidential, where unauthorized disclosure could reasonably be expected to cause damage to national security; Secret, serious damage; and Top Secret, exceptionally grave damage. Only officials with original classification authority may classify information originally, and they must set a declassification date or event, normally no more than 10 years and in most cases at most 25 years out. Separately, sensitive but unclassified information is handled under the Controlled Unclassified Information (CUI) program created by Executive Order 13556 and implemented by 32 CFR Part 2002, with categories listed in the National Archives CUI Registry. Federal systems are also categorized by impact under FIPS 199: low, moderate or high for each of confidentiality, integrity and availability, with the overall category taking the highest of the three, the so-called high-water mark.
For defense contractors, CUI handling is enforced through DFARS clause 252.204-7012 and the Cybersecurity Maturity Model Certification (CMMC) program, which requires the NIST SP 800-171 controls, now in Revision 3 (May 2024), although the CMMC rule initially references Revision 2. The FIPS 199 high-water mark drives the NIST SP 800-53 control baseline selected for a system, which lesson 11 returns to. State governments have their own schemes for state information, often modeled on the federal low, moderate and high categories.
Commercial classification
Private organizations are free to design their own schemes, and most use three to five levels. A common four-level scheme is public, internal, confidential and restricted. Public information can be released to anyone without harm: published marketing material, press releases and public filings. Internal information is meant for employees and trusted partners, and disclosure would cause minor harm: the staff directory, internal policies and routine project notes. Confidential information would cause significant harm if disclosed: customer lists, contracts, unreleased financials, most personal information. Restricted information would cause severe harm: merger plans, trade secrets, encryption keys, authentication secrets and large sets of sensitive personal data. Other common names include sensitive, private and highly confidential; the names matter less than clear definitions.
| Level | Harm if disclosed | Examples | Typical handling |
|---|---|---|---|
| Public | None | Press releases, published prices | No restrictions once approved for release |
| Internal | Minor | Policies, staff directory, meeting notes | Staff and contracted partners only |
| Confidential | Significant | Customer lists, contracts, personal information | Need to know, encryption in transit and on portable media |
| Restricted | Severe | Merger plans, trade secrets, keys, large health data sets | Named access lists, encryption everywhere, logging, no personal devices |
The number of levels is a trade-off. Too few, and very different kinds of information end up with the same controls, so either the sensitive information is under-protected or the routine information is over-protected. Too many, and people cannot tell the levels apart, so they guess, usually by choosing the highest level to be safe, a problem called over-classification. Over-classification wastes money, obstructs sharing and erodes respect for the scheme. Most organizations find that three or four levels, plus special handling markings for particular categories such as personal information or payment card data, strike the right balance.
Government and commercial schemes differ in emphasis. Government schemes center on the national interest and harm to the state, are backed by law and security clearances, and include formal declassification. Commercial schemes center on harm to the business and its customers, are backed by policy and contract, and usually rely on periodic review rather than automatic declassification. Both share the same core idea: the category sets the controls, and the harm from compromise sets the category.
Making classification decisions
Classification starts with criteria that describe harm in concrete terms, so that two people looking at the same information reach the same answer. Good criteria combine the type of information, legal and contractual obligations, the volume involved and the context. A single customer's email address may be internal; a million email addresses with purchase histories are confidential or restricted, because aggregation increases harm. Combining individually low-value pieces of information to reveal something sensitive is called the aggregation problem, and the related inference problem arises when someone deduces sensitive facts from less sensitive ones, such as inferring a merger from unusual travel and legal bills.
Worked problem
Classifying four data sets
Using the four-level scheme above, classify: (a) the cafeteria menu; (b) an engineering team's internal wiki; (c) a spreadsheet of 800 employees with names, home addresses and salaries; (d) the private signing key for the company's software updates.
Show solution
- (a) Disclosure causes no harm: public.
- (b) Routine internal knowledge with minor harm if leaked: internal, unless pages contain credentials or design secrets, which should be moved and classified higher.
- (c) Personal information about many people, with salary data that could cause significant harm: confidential at least; many schemes would make it restricted because of the volume and sensitivity.
- (d) Compromise would let attackers sign malware as the company, a severe integrity and reputational harm: restricted.
Answer: Public, internal, confidential or restricted, and restricted. Note that (d) is classified high mainly for integrity, not confidentiality of its content.
Classification is not permanent. Information should be reviewed when circumstances change: a product launch makes design details public, a contract ends, a legal hold is lifted, or the data is anonymized. The owner should set review points, and the scheme should allow downgrading as well as upgrading. Government schemes handle this through declassification rules; commercial schemes should build reviews into records management, covered in lesson 9.
Labeling and marking
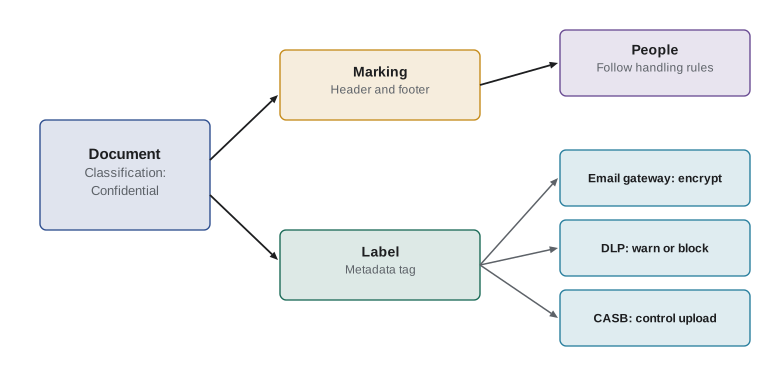
A classification decision is only useful if people and systems can see it. Marking is the human-readable indication of classification on the information itself: a header and footer on a document, a banner on a screen, a stamp on a printed page or a sticker on a removable drive. Labeling usually refers to machine-readable attributes attached to the information, such as metadata in a file, a tag on a cloud storage object or a sensitivity label in an email system, which tools such as data loss prevention can act on. Many sources use the two terms loosely; the important distinction is between what people read and what systems read, and a mature program uses both.
Modern office suites and cloud platforms support sensitivity labels that can be applied manually, recommended automatically based on content, or applied automatically by policy. A label can trigger protections: encryption, watermarks, restrictions on forwarding or printing, and blocking upload to unapproved services. Automatic labeling reduces reliance on users remembering, but it can mislabel, so a common design is to recommend labels based on content and let users confirm or justify a change, with logging. Unlabeled information should have a default, and the safe default is usually internal rather than public.
Physical media and equipment need marking too. Backup tapes, removable drives and printed reports should carry their classification so that couriers, cleaners and disposal staff know how to handle them. Systems can be labeled with the highest classification of the data they process, which helps operators and auditors, though some organizations avoid conspicuous labels on equipment in public areas because a sticker saying restricted tells a thief exactly what to steal.
Classification across borders and partners
Organizations that share information with partners, suppliers or other governments need to map their levels to the other party's. A contract or information-sharing agreement should state how each level will be treated, so that a supplier does not treat a customer's restricted data as merely internal. The Traffic Light Protocol, version 2.0 published by FIRST in 2022, is a widely used simple scheme for sharing threat intelligence: TLP:RED (named recipients only), TLP:AMBER and TLP:AMBER+STRICT (limited sharing within organizations), TLP:GREEN (community sharing) and TLP:CLEAR (no restriction). It is a sharing protocol, not a full classification scheme, but it illustrates how agreed markings let different organizations handle information consistently.
Thinking like a manager
On the exam, classification questions often test who decides and on what basis. The owner classifies, using criteria based on harm and legal obligations, and the custodian implements the resulting controls. If a scenario describes inconsistent handling, the fix is usually clearer criteria, training and labeling tools rather than more technology alone. If a scenario describes over-classification slowing the business, the answer is to refine the scheme and criteria, not to abandon classification. And when information is combined, remember aggregation: the whole can be more sensitive than any of its parts.
Common mistakes
MistakeClassifying information by who created it or how senior they are.
InsteadClassify by the harm from compromise and by legal obligations.
MistakeUsing many fine-grained levels to be precise.
InsteadThree or four well-defined levels plus special markings are easier to apply consistently.
MistakeMarking everything restricted to be safe.
InsteadOver-classification wastes money and erodes respect for the scheme.
MistakeTreating classification as permanent.
InsteadReview and downgrade or upgrade when circumstances change.
MistakeRelying only on human-readable markings.
InsteadAdd machine-readable labels so tools can enforce handling rules.
Summary and key terms
- Classification places assets in categories that carry defined protections, making controls proportionate to harm.
- Decisions consider harm to confidentiality, integrity and availability, plus legal and contractual obligations.
- US national security information is Confidential, Secret or Top Secret under EO 13526; sensitive unclassified information is CUI; FIPS 199 rates impact low, moderate or high.
- Commercial schemes typically use three to five levels such as public, internal, confidential and restricted.
- Aggregation and inference can make combined information more sensitive than its parts.
- Marking is for people and labeling is for systems; both should show the same classification.
- The owner classifies and reviews; custodians implement the controls.
- Classification
- Placing an asset in a category based on the harm from its compromise.
- Over-classification
- Assigning a higher level than the harm justifies.
- Aggregation
- Combining less sensitive items into a more sensitive whole.
- Inference
- Deducing sensitive facts from less sensitive information.
- Marking
- A human-readable indication of classification on information or media.
- Label
- A machine-readable classification attribute attached to information.
- Protected B
- A Canadian government designation for information whose compromise could cause serious injury outside the national interest.
- CUI
- Controlled Unclassified Information, the US federal program for sensitive unclassified information.
- High-water mark
- Categorizing a system at the highest impact level of any of its properties.
- Traffic Light Protocol
- A simple marking scheme for sharing information, from TLP:RED to TLP:CLEAR.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What should drive a classification decision?
Show answer
The harm from compromise and any legal or contractual obligations.
What is the difference between classified information and CUI?
Show answer
Classified information concerns damage to national security under EO 13526; CUI is sensitive but unclassified information under 32 CFR 2002.
Why can too many classification levels backfire?
Show answer
People cannot tell them apart and tend to over-classify.
Give an example of aggregation increasing sensitivity.
Show answer
One customer's email is low risk; a million with purchase histories is high risk.
What is the difference between marking and labeling?
Show answer
Markings are read by people; labels are read by systems.
What is a safe default for unlabeled information?
Show answer
Internal, not public.
Why might a signing key be restricted even though its content is meaningless to people?
Show answer
Its compromise would allow forged software, a severe integrity harm.
When should classification be reviewed?
Show answer
At set points and when circumstances change, such as a product launch or contract end.
What does TLP:RED mean?
Show answer
Sharing is limited to the named recipients.
Who implements the controls that follow from a classification?
Show answer
The custodian, on the owner's behalf.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.