
CISSP-114 · Lesson 12 of 12 · 26 min
Capstone: designing IAM for an organization
This capstone brings the course together by designing an identity and access management program for an invented organization, Larchmere Mutual, a regional insurer with about 1,600 employees, 400 independent brokers who use a partner portal and 120,000 policyholders who use a customer portal. Larchmere is fictional, but its problems are typical of the findings security managers meet in practice. Work through each section as if you were presenting to its executive committee, then use the final section to prepare for Domain 5 questions on the exam.
Current state
An assessment of Larchmere's identity environment produced the following findings. Employees sign in with passwords and push MFA to a cloud identity provider for about half of the 70 business applications; the rest have local accounts. The on-premises Active Directory synchronizes to the cloud through a server administered by a contractor. Thirty-one people are permanent members of Domain Admins, and local administrator passwords are the same on every workstation. Leavers are processed when managers email the help desk; a reconciliation found 146 enabled accounts belonging to former staff, eleven used in the past six months. Brokers share logins within brokerages. The customer portal uses passwords with security questions for recovery. There are 940 service accounts and API keys, and nobody can say who owns two-thirds of them. Access reviews are annual spreadsheets that come back 98 % approved.
| Finding | Access control step affected | Risk |
|---|---|---|
| Half of applications outside SSO, with local accounts | Authentication, leaver revocation | Weak passwords; access survives departure |
| Push MFA only | Authentication | Adversary-in-the-middle phishing and fatigue attacks |
| 31 permanent domain administrators; identical local admin passwords | Authorization (privileged) | One compromise spreads to the whole domain |
| Leavers processed by email; 146 former staff still enabled | Provisioning life cycle | Former staff and attackers using dormant accounts |
| Shared broker logins | Identification and accountability | No attribution of broker actions; leaver risk at brokerages |
| Security questions for customer recovery | Recovery and proofing | Account takeover using public or breached data |
| 940 non-human identities, most unowned | Identification and authorization | Leaked or abused keys with broad rights |
| Spreadsheet reviews, 98 % approved | Accounting and review | Privilege creep and rubber-stamping |
Requirements and constraints
Requirements come from risk, regulation and the business. The board wants to reduce the chance of a major breach through stolen credentials, which the insurer's own claims data shows to be the leading cause of cyber losses in its industry. Brokers must be able to quote and bind policies quickly. Customers must be able to recover accounts without calling, but the claims team reports fraudsters changing payout details after taking over accounts. Auditors require evidence of timely removal of leavers and periodic review of access to financial and claims systems.
As a US insurer licensed in several states, Larchmere must meet state insurance data security laws modeled on the NAIC Insurance Data Security Model Law, which require an information security program with access controls and, in many states, multifactor authentication. Where it operates in New York, NYDFS Part 500 as amended requires multifactor authentication for all individuals accessing its information systems, privileged access management and at least annual access reviews. The Gramm-Leach-Bliley Act's privacy and safeguards requirements also apply to customer financial information, and state biometric laws such as Illinois BIPA would govern any biometric customer verification. Checked October 2026.
Target architecture
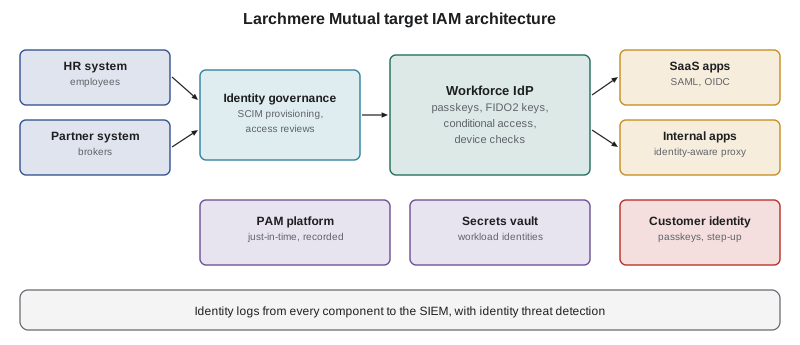
The target architecture follows the principles of this course. A single cloud identity provider becomes the front door for employees and brokers, with every application federated through SAML or OpenID Connect, or placed behind an identity-aware proxy where it cannot federate. The HR system drives employee joiners, movers and leavers; a partner management system drives broker identities, with each brokerage's administrator able to manage its own users under delegated administration and every broker given an individual account. The customer portal uses a separate customer identity service, with passkeys offered to all customers, risk-based step-up and strong recovery. Privileged access goes through a PAM platform with just-in-time elevation. Non-human identities move to managed identities and a secrets vault. Identity logs from all components flow to the SIEM with identity threat detections.
| Population | Identification | Authentication | Authorization | Life cycle |
|---|---|---|---|---|
| Employees | Unique ID from HR | Passkeys on managed devices (AAL2, phishing-resistant) | Roles by function plus attributes for claims region | HR-driven JML with SCIM |
| Administrators | Separate admin accounts | Device-bound FIDO2 keys (AAL3) on privileged workstations | Just-in-time elevation through PAM | Quarterly review; break-glass sealed |
| Brokers | Individual accounts per broker | Passkeys or app-based MFA with number matching, moving to passkeys | Scoped to own brokerage's clients | Brokerage admin manages; annual attestation; inactivity expiry |
| Customers | Email plus policy number at registration | Passkeys offered; risk-based step-up | Own policies only; step-up for payout changes | Proofing with policy data and document check for high-risk changes |
| Workloads | Managed identities, owners recorded | Short-lived platform credentials; no stored keys | Least privilege, right-sized with CIEM | Owner review twice yearly |
Prioritizing the roadmap
With limited budget and staff, Larchmere must sequence the work. A simple risk-reduction model helps the executive committee compare options. The annualized loss expectancy, ALE, is the expected number of incidents per year, the annualized rate of occurrence, ARO, times the single loss expectancy, SLE:
The figures below are illustrative estimates a team might produce from industry data and its own incident history. The point is not precision but a defensible ranking.
import random
random.seed(2026)
# Illustrative annual rates and single-loss estimates for credential-driven incidents
scenarios = {
    'workforce account takeover': (0.9, 1_800_000),
    'privileged credential compromise': (0.25, 6_500_000),
    'leaver or dormant account misuse': (0.4, 600_000),
    'customer account takeover and payout fraud': (6.0, 45_000),
    'leaked non-human credential': (0.5, 900_000),
}
# Estimated fraction of each risk removed by each initiative, and its yearly cost
initiatives = {
    'phishing-resistant MFA and full SSO': ({'workforce account takeover': 0.75, 'leaver or dormant account misuse': 0.3}, 420_000),
    'PAM with just-in-time and tiering': ({'privileged credential compromise': 0.7, 'workforce account takeover': 0.1}, 380_000),
    'HR-driven JML and reconciliation': ({'leaver or dormant account misuse': 0.8}, 150_000),
    'customer passkeys and risk-based step-up': ({'customer account takeover and payout fraud': 0.7}, 200_000),
    'workload identities and secrets vault': ({'leaked non-human credential': 0.7}, 160_000),
}
base = {k: aro * sle for k, (aro, sle) in scenarios.items()}
print(f'Baseline ALE: ${sum(base.values()):,.0f}')
rows = []
for name, (effects, cost) in initiatives.items():
    saved = sum(base[k] * f for k, f in effects.items())
    rows.append((saved - cost, name, saved, cost))
for net, name, saved, cost in sorted(rows, reverse=True):
    print(f'{name:42s} ALE reduced ${saved:>10,.0f}  cost ${cost:>8,.0f}  net ${net:>10,.0f}')
# Uncertainty: vary every estimate by +/-40 % and count how often the top initiative stays first
wins = 0
for _ in range(2000):
    b = {k: aro * sle * random.uniform(0.6, 1.4) for k, (aro, sle) in scenarios.items()}
    scores = {n: sum(b[k] * f * random.uniform(0.6, 1.4) for k, f in e.items()) - c for n, (e, c) in initiatives.items()}
    wins += max(scores, key=scores.get) == sorted(rows, reverse=True)[0][1]
print(f'Top initiative stays first in {wins / 2000:.0%} of 2,000 simulations')Baseline ALE: $4,205,000 PAM with just-in-time and tiering ALE reduced $ 1,299,500 cost $ 380,000 net $ 919,500 phishing-resistant MFA and full SSO ALE reduced $ 1,287,000 cost $ 420,000 net $ 867,000 workload identities and secrets vault ALE reduced $ 315,000 cost $ 160,000 net $ 155,000 HR-driven JML and reconciliation ALE reduced $ 192,000 cost $ 150,000 net $ 42,000 customer passkeys and risk-based step-up ALE reduced $ 189,000 cost $ 200,000 net $ -11,000 Top initiative stays first in 53% of 2,000 simulations
In this illustration, privileged access management and phishing-resistant MFA with full SSO dominate the ranking, each removing about $1.3 million of expected loss, far ahead of the rest. They are so close that the simulation swaps their order about half the time, which tells the committee to treat them as joint first priorities rather than argue over which comes first. HR-driven deprovisioning saves less in expected loss but is cheap, closes an audit finding and is a prerequisite for much else, so a sensible roadmap runs it in parallel. Customer passkeys show a small net cost in this narrow model, which counts only direct fraud losses; customer trust, regulatory expectations and the help desk cost of security-question recovery could justify them, and a manager would say so. A manager presents the ranking together with dependencies, regulatory deadlines and quick wins, not as a mechanical answer.
| Phase | Timing | Initiatives | Measures of success |
|---|---|---|---|
| 1. Stop the bleeding | Months 0 to 3 | Disable the 146 former-staff accounts; cut Domain Admins to Tier 0 staff; deploy unique local admin passwords; number matching on push; seal break-glass accounts | Zero enabled former-staff accounts; fewer than 6 domain admins |
| 2. Foundations | Months 3 to 9 | HR-driven JML with SCIM; federate remaining applications; PAM vault and session recording; privileged workstations and FIDO2 for admins | Leavers removed within 1 hour; 95 % of applications behind SSO |
| 3. Strong authentication everywhere | Months 6 to 15 | Passkeys for all employees; individual broker accounts with MFA; customer passkeys and risk-based step-up; retire security questions | Phishing-resistant sign-ins above 90 %; customer takeover fraud halved |
| 4. Least privilege at scale | Months 9 to 18 | Just-in-time elevation; role redesign and peer analysis; risk-focused reviews; workload identities, vault and CIEM; ITDR detections | Standing admin privilege near zero; review revocations completed within 5 days; no unowned non-human identities |
Worked problem
Answering the board
A board member asks: we already have MFA, so why spend $420,000 a year on a different kind? Prepare a two-minute answer.
Show solution
- Our current MFA, push approval, stops simple password attacks but not the phishing kits criminals now use, which relay the login and steal the session after the user approves.
- Phishing-resistant passkeys and security keys are bound to our real websites, so a fake site cannot use the response; government agencies and many financial institutions now require this method.
- Our estimate is that this removes about three-quarters of the expected loss from employee account takeover, the most likely route to a major breach, and it also removes most password resets, which cost the help desk time.
- We will measure success by the share of sign-ins using phishing-resistant methods and by phishing incidents that fail to produce access.
Answer: Translate the control into the attack it stops, the loss it avoids and how progress will be measured. Boards fund risk reduction they understand.
Strategy for Domain 5 questions
Domain 5 questions reward the same disciplined thinking used in this capstone. First, identify which access control step the scenario is about: identification, authentication, authorization, accountability or life cycle. Second, look for the root cause rather than the symptom: a former employee logging in is a deprovisioning process failure, not merely a bad account. Third, prefer preventive, systemic controls over detective or one-off ones, unless the question asks what to do first in an incident. Fourth, apply the core principles: unique identities, phishing-resistant authentication, least privilege, separation of duties, just-in-time privilege, automated life cycle management and reviewed logs.
| If the question mentions | Think of |
|---|---|
| Shared accounts, no attribution | Unique identification; accountability |
| Phishing, relayed codes, push fatigue | Phishing-resistant MFA: FIDO2, passkeys, smart cards |
| Owner decides | Discretionary access control |
| Labels, clearance, compartments | Mandatory access control and dominance |
| Job functions, conflicting duties | Role-based control with static or dynamic separation of duties |
| Attributes, context, device health | ABAC, risk-based and conditional access |
| Tickets, KDC, clock skew | Kerberos |
| Assertions, IdP and SP | SAML federation |
| Delegated API access, scopes | OAuth 2.0; with identity, OpenID Connect |
| Former staff, accumulated access | Leaver automation; mover removal; access reviews |
| Administrators, root, break-glass | PAM, just-in-time, session recording |
| FAR, FRR, CER | Biometric accuracy; lower CER is better |
Watch for the distractors that appear in many questions: answers that strengthen passwords when the problem is phishing, answers that add monitoring when a preventive control is available, answers that fix one account when the process is broken, and answers that are technically correct but skip governance, such as deploying a tool before defining ownership and policy. As in every domain, the best answer is usually the one a responsible manager would choose: risk-based, systemic, documented and aligned with the organization's objectives.
Thinking like a manager
An IAM program succeeds when identity is treated as core infrastructure with business ownership, not as a help desk function. It needs an authoritative source of truth, a single strong front door, least privilege enforced by architecture, privileged access under tight control, machine identities governed like human ones and evidence that all of this works. Larchmere's roadmap shows that the work can be sequenced so that each phase reduces risk measurably, and that the case for investment is made in terms of attacks stopped and losses avoided.
Common mistakes
MistakeStarting an IAM program by buying tools before defining sources of truth and ownership.
InsteadDefine authoritative sources, owners and policy first, then select tools that implement them.
MistakeTreating brokers, customers and workloads exactly like employees.
InsteadDesign identification, authentication, authorization and life cycle for each population.
MistakePresenting the board with technical features instead of risk reduction.
InsteadExplain the attacks stopped, expected loss avoided and the measures of success.
MistakeFixing the symptom, such as one dormant account, and moving on.
InsteadFix the process that created it and evidence the fix.
MistakeChoosing more monitoring when a preventive control is available.
InsteadPrefer preventive, systemic controls, backed by monitoring.
Summary and key terms
- Map assessment findings to the access control steps to see where the program is weakest.
- Requirements combine risk, regulation and business needs; Canadian and US regimes both expect strong authentication, least privilege and reviews.
- Design identity separately for employees, administrators, partners, customers and workloads.
- ALE = ARO times SLE gives a defensible way to rank IAM investments; test rankings against uncertainty.
- Sequence the roadmap: quick wins, foundations, strong authentication, then least privilege at scale.
- Explain investments to boards in terms of attacks stopped and losses avoided.
- For the exam, identify the access control step, find the root cause and choose systemic, preventive controls.
- Annualized loss expectancy
- Expected yearly loss from a risk: ARO times SLE.
- Annualized rate of occurrence
- Expected number of times a loss event occurs per year.
- Single loss expectancy
- Expected cost of one occurrence of a loss event.
- Customer identity and access management
- Identity services designed for customers, balancing security with ease of use.
- Delegated administration
- Allowing a partner's administrator to manage its own users within limits.
- Authoritative source
- The system of record that determines whether an identity should exist.
- Identity-aware proxy
- A gateway that enforces identity-based access to applications.
- Quick win
- A low-cost action that reduces risk immediately.
- Roadmap
- A sequenced, resourced plan of initiatives with measures of success.
- Root cause
- The underlying process or design failure that allowed a problem to occur.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Which finding at Larchmere most directly undermines accountability for brokers?
Show answer
Shared broker logins.
What is the ALE formula?
Show answer
ALE equals ARO times SLE.
Compute the ALE for a risk with ARO 0.25 and SLE $6,500,000.
Show answer
$1,625,000.
Why run HR-driven JML early even if its loss reduction is smaller?
Show answer
It is cheap, closes an audit finding and is a prerequisite for other controls.
What authentication fits Larchmere administrators?
Show answer
Device-bound FIDO2 security keys at AAL3 on privileged workstations.
What replaces security questions for customer recovery?
Show answer
Passkeys with risk-based step-up and stronger proofing for high-risk changes.
Name one quick win in phase 1.
Show answer
Disabling former-staff accounts, or deploying unique local admin passwords.
What is the first thing to identify in a Domain 5 question?
Show answer
Which access control step the scenario concerns.
Why test a ranking with simulation?
Show answer
To see whether conclusions survive uncertainty in the estimates.
What should a board explanation focus on?
Show answer
Attacks stopped, losses avoided and how success will be measured.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.