
CISSP-117 · Lesson 12 of 12 · 25 min
Capstone: a secure development program for an organization, with Domain 8 exam strategy
This final lesson brings the course together. We design a secure development program for Ridgeline Payments, decide how to measure whether it works, and plan its first eighteen months. Then we turn to the exam: how Domain 8 questions are framed, the traps they set, and how a manager's perspective helps choose the best answer. As throughout the course, this is independent study material, not produced or endorsed by ISC2, and every question is original.
Where Ridgeline stands
Earlier lessons revealed Ridgeline's strengths and gaps. It has a modern delivery pipeline with automated builds, branch protection and peer review (Lessons 3 and 4). Its build and deployment practices scored highest in the SAMM self-assessment, while threat assessment and architecture assessment scored lowest (Lesson 3). Its SAST rollout generated too much noise (Lesson 9). A staging environment held real customer data (Lesson 4), a penetration test found an insecure direct object reference exposing other merchants' refunds (Lesson 7), bank account numbers were readable by many services (Lesson 8), and developers had begun using consumer AI tools with company code (Lesson 11). The bank partner wants evidence of a mature program within eighteen months, and the company may expand into the EU market, where the Cyber Resilience Act would apply.
Program structure
A secure development program needs the same governance elements as any security program: a policy approved by senior management, standards that make the policy concrete, defined roles, resources, a plan, metrics and regular reporting. For Ridgeline the program charter assigns accountability as follows. The chief technology officer owns the program jointly with the chief information security officer; product owners own the security risk of their products; the application security team sets standards, provides tooling and training, performs expert reviews and reports metrics; security champions lead day-to-day practice in each team; and the platform team owns the security of the pipeline and environments.
| Program element | Ridgeline's design | Lesson |
|---|---|---|
| Policy and standards | Secure development policy; secure coding standard per language; component and AI use standards | 1, 5, 10, 11 |
| Requirements | ASVS level 2 as baseline for customer-facing services; abuse cases for payment features | 1 |
| Design | Threat modeling triggers; design review for new services and authorization changes | 2 |
| Ecosystem | Repository controls, secrets management, ephemeral builds, SLSA Build L2 target, signed artifacts | 4 |
| Coding | Approved patterns for queries, encoding, authentication, sessions, cryptography and logging | 5, 6 |
| Data | Least-privilege database accounts; tokenization of bank details; masked test data | 4, 8 |
| Testing | Peer review, tuned SAST, SCA with reachability, DAST in staging, fuzzing for parsers, annual penetration tests | 9 |
| Supply chain | SBOM per build, component approval, internal proxy, VEX for customers | 10 |
| Acquisition and AI | Supplier assessment, security contract schedule, approved AI assistant with policy | 11 |
| Response | Vulnerability disclosure program, severity-based fix deadlines, CRA-ready reporting process | 9, 10 |
| Measurement | Metrics dashboard, six-monthly SAMM reassessment, annual external review | 12 |
Measuring effectiveness
The CISSP objective on assessing the effectiveness of software security includes auditing and logging of changes and risk analysis and mitigation, and in practice it depends on good metrics. Metrics should answer management's questions: Are we finding problems early? Are we fixing them fast enough? Is the risk going down? Are the controls actually operating? A small, stable set of metrics, reported consistently over time, is more useful than a large dashboard nobody reads. Metrics fall into three groups.
| Type | Example metrics | What they show |
|---|---|---|
| Coverage (are controls operating?) | Share of services with a current threat model; share of repositories with SAST, SCA and secrets scanning; share of releases with SBOMs | Whether the program reaches everything it should |
| Efficiency (are we fast?) | Mean and median time to remediate by severity; percentage fixed within deadline; age of open findings | Whether vulnerabilities are handled within risk appetite |
| Outcome (is risk falling?) | Vulnerabilities found in production versus before release (escape rate); severe findings per release; incidents caused by software defects | Whether the program actually makes software safer |
from datetime import date
from statistics import mean, median
# Remediation performance and escape rate for one quarter (synthetic findings)
DEADLINE = {'critical': 7, 'high': 30, 'medium': 90}
findings = [  # severity, found where, opened, closed (None = still open at 2026-09-30)
    ('critical', 'production',  date(2026, 7, 3),  date(2026, 7, 6)),
    ('critical', 'pre-release', date(2026, 8, 14), date(2026, 8, 25)),
    ('high',     'pre-release', date(2026, 7, 1),  date(2026, 7, 20)),
    ('high',     'production',  date(2026, 7, 9),  date(2026, 8, 28)),
    ('high',     'pre-release', date(2026, 8, 2),  date(2026, 8, 19)),
    ('high',     'pre-release', date(2026, 9, 1),  None),
    ('medium',   'pre-release', date(2026, 7, 15), date(2026, 9, 2)),
    ('medium',   'production',  date(2026, 6, 20), None),
    ('medium',   'pre-release', date(2026, 8, 5),  date(2026, 8, 30)),
    ('medium',   'pre-release', date(2026, 9, 10), date(2026, 9, 22)),
]
end = date(2026, 9, 30)
for sev in DEADLINE:
    rows = [f for f in findings if f[0] == sev]
    closed = [(c - o).days for s, w, o, c in rows if c]
    on_time = sum(1 for s, w, o, c in rows if ((c or end) - o).days <= DEADLINE[sev] and c)
    overdue_open = sum(1 for s, w, o, c in rows if not c and (end - o).days > DEADLINE[sev])
    print(f'{sev:8s} n={len(rows)}  mean {mean(closed):5.1f} d  median {median(closed):4.1f} d  '
          f'on time {on_time}/{len(rows)}  open past deadline {overdue_open}')
prod = sum(1 for f in findings if f[1] == 'production')
print(f'Escape rate: {prod}/{len(findings)} = {prod / len(findings):.0%} of findings were first found in production')critical n=2 mean 7.0 d median 7.0 d on time 1/2 open past deadline 0 high n=4 mean 28.7 d median 19.0 d on time 2/4 open past deadline 0 medium n=4 mean 28.7 d median 25.0 d on time 3/4 open past deadline 1 Escape rate: 3/10 = 30% of findings were first found in production
The numbers tell a story management can act on. Critical findings are fixed quickly, though one took longer than the seven-day target; one high finding found in production took 50 days, far beyond its deadline; and a medium production finding is still open after more than three months. The escape rate of 30 % shows that too many problems are first found after release, which is consistent with the weak design-phase practices identified earlier. Means and medians are both reported because a few long-running items can make the mean misleading.
Change auditing is also part of assessing effectiveness. The pipeline and repository logs described in Lesson 4 should be reviewed to confirm that controls cannot be bypassed: sample production changes each quarter and verify that each has a linked work item, an independent approval, passing checks and a deployment record; investigate any change that reached production outside the pipeline. Findings from these audits feed back into the risk register, where residual risks are analyzed and either mitigated or formally accepted by their owners.
An eighteen-month roadmap
Worked problem
Ridgeline's roadmap
Turn the gaps identified across the course into a realistic plan that satisfies the bank partner and prepares for possible EU expansion.
Show solution
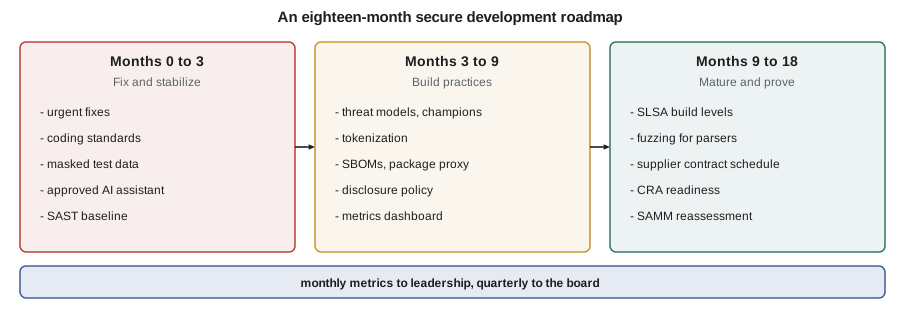
- Months 0 to 3: approve the policy and coding standards; fix the IDOR and stored XSS and add authorization tests; remove real data from staging and provide masked datasets; approve an enterprise AI assistant with a use policy; baseline and tune SAST.
- Months 3 to 9: launch threat modeling triggers and train all twelve champions; tokenize bank details; generate SBOMs for every build and stand up the internal package proxy; publish a vulnerability disclosure policy; start the metrics dashboard.
- Months 9 to 18: reach SLSA Build L2 across services and L3 for the payments core; add fuzzing for file import parsers; adopt the supplier security schedule for all new contracts; prepare a CRA readiness assessment and reporting procedure; reassess SAMM to show progress to the bank partner.
- Throughout: report coverage, efficiency and outcome metrics monthly to the CTO and CISO and quarterly to the board.
Answer: The roadmap fixes urgent exposures first, then strengthens the weak design and supply chain practices, and builds the evidence the bank partner and future regulators will ask for.
For Ridgeline in Denver, the roadmap also maps to US expectations: the Gramm-Leach-Bliley Act Safeguards Rule, which requires a written information security program including secure development practices for in-house applications; the bank partner's obligations under the 2023 interagency guidance on third-party relationships, which flow down to Ridgeline; and the NIST SSDF, which many customers still use as a reference even after the federal attestation requirement was rescinded in January 2026.
Domain 8 on the exam
Domain 8 carries about 10 % of the weight in the April 2024 outline. Its questions rarely ask you to read code. They test whether you understand where security fits in development, what each technique does and does not do, and what a responsible manager would choose. The following patterns recur.
| Question pattern | What usually makes an answer best |
|---|---|
| When should security be involved? | As early as possible: requirements and design, with continued involvement through operations |
| Which testing technique fits? | Match the technique to the stage and the weakness: SAST early on code, DAST on running systems, SCA for components, fuzzing for input handlers |
| A vulnerability is found; what next? | Assess and prioritize by risk, fix the root cause, check for misuse, and improve the process that let it through |
| A vendor makes security claims | Seek independent evidence, read it critically, and put requirements into the contract |
| Which principle or model is shown? | Recognize the definition: complete mediation, least privilege, ACID, polyinstantiation, CMMI levels, SAMM versus BSIMM |
| Speed versus security | Integrate security into the process rather than adding a late gate or bypassing controls |
| Who decides? | The business owner accepts risk; security advises; developers fix; management sets policy |
Watch for distractors that are technically true but not the best managerial choice. An answer that adds a web application firewall may reduce risk, but fixing the code is usually better. An answer that requires the security team to review every change may sound rigorous, but it does not scale and removes ownership from developers. An answer that bans a tool or practice outright is rarely best when a governed alternative exists. When two answers seem right, prefer the one that addresses root cause, is earliest in the life cycle, assigns accountability correctly and leaves evidence. And as in every domain, human safety and legal obligations come first.
Finally, connect Domain 8 with the rest of the CISSP. Secure design principles come from Domain 3; identity and session controls from Domain 5; testing programs from Domain 6; change and vulnerability management from Domain 7; and governance, risk, supply chain and legal requirements from Domain 1. Exam scenarios often cross these boundaries, and a candidate who sees software security as part of the whole security program will choose better answers.
Common mistakes
MistakeRunning a secure development program without metrics.
InsteadReport a small, stable set of coverage, efficiency and outcome metrics over time.
MistakeReporting only mean remediation time.
InsteadReport means, medians and on-time rates, because a few long items distort the mean.
MistakeTrying to fix every gap at once.
InsteadFix urgent exposures first, then build practices in a staged roadmap.
MistakeTreating the program as the security team's project.
InsteadAssign joint ownership to technology and security leaders, with product owners accountable for product risk.
MistakeChoosing the most technical answer on the exam.
InsteadChoose the answer a responsible manager would choose: root cause, early, accountable and evidenced.
MistakeStudying Domain 8 in isolation.
InsteadLink it to design, identity, testing, operations and governance topics in the other domains.
Summary and key terms
- A secure development program needs policy, standards, roles, resources, a plan, metrics and reporting.
- Ownership is shared: technology and security leaders own the program, product owners own product risk, and champions lead daily practice.
- Coverage, efficiency and outcome metrics show whether controls operate, whether fixes are timely and whether risk is falling.
- Escape rate, the share of findings first found in production, indicates how well early practices work.
- Change audits confirm that pipeline controls cannot be bypassed and feed the risk register.
- A staged roadmap fixes urgent exposures, then builds practices, then matures and proves them.
- On the exam, prefer answers that address root cause early, assign accountability correctly and leave evidence.
- Secure development program
- The governance, practices and measurement that integrate security into software development.
- Coverage metric
- A measure of how much of the environment a control reaches.
- Mean time to remediate
- The average time from discovery of a vulnerability to its fix.
- Escape rate
- The share of defects or vulnerabilities first discovered in production.
- Remediation deadline
- The maximum time allowed to fix a finding, usually set by severity and exposure.
- Change audit
- A review of a sample of changes to confirm required controls were followed.
- Residual risk
- The risk remaining after controls are applied.
- Roadmap
- A staged plan of improvements with milestones over time.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name the governance elements of a secure development program.
Show answer
Policy, standards, roles, resources, plan, metrics and reporting.
Who should own Ridgeline's program?
Show answer
The CTO and CISO jointly, with product owners accountable for product risk.
Give one coverage, one efficiency and one outcome metric.
Show answer
For example: share of services with threat models; median time to remediate; escape rate.
Why report medians as well as means?
Show answer
A few long-running items can distort the mean.
What does a high escape rate suggest?
Show answer
Early-phase practices are not catching enough problems before release.
What does a quarterly change audit check?
Show answer
That sampled changes had work items, independent approval, passing checks and pipeline deployment.
What should the first three months of the roadmap focus on?
Show answer
Urgent exposures and foundational standards.
What weight does Domain 8 carry in the April 2024 outline?
Show answer
About 10 %.
Why is fixing code usually better than adding a WAF rule?
Show answer
It removes the root cause rather than compensating for it.
Which CISSP domains connect most with Domain 8?
Show answer
Domain 3 (design), 5 (identity), 6 (testing), 7 (operations) and 1 (governance and supply chain).
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.