
CISSP-117 · Lesson 3 of 12 · 26 min
Development methodologies, DevSecOps and maturity models
How an organization builds software shapes where and how security can be applied. A defense contractor building flight software under a fixed contract works very differently from Ridgeline's teams, which release small changes to production many times a day. Security practices that suit one will fail in the other. The CISSP outline expects you to recognize the main development methodologies, understand how security fits each, and know the maturity models and frameworks that organizations use to assess and improve their secure development practices.
CMPUT-301 Lesson 2 covers software process models from an engineering point of view, and Lesson 11 of that course covers continuous integration, delivery and DevOps in practice. This lesson takes the security manager's view: what each model implies for controls, evidence and governance.
Waterfall and its variants
The waterfall model moves through phases in sequence: requirements, design, implementation, verification and maintenance, with each phase completed and approved before the next begins. Its strengths for security are predictability and documentation. Requirements are fixed early, design reviews and formal sign-offs are natural, and auditors find abundant evidence. Its weaknesses are rigidity and late feedback. Security problems discovered in testing may require rework of designs approved months earlier, and changing threats are hard to absorb once requirements are frozen.
The V-model pairs each development phase with a corresponding testing phase: requirements with acceptance testing, system design with system testing, detailed design with integration testing and coding with unit testing. It makes explicit that every requirement, including every security requirement, needs a matching verification activity. The spiral model, introduced by Barry Boehm, repeats cycles of planning, risk analysis, engineering and evaluation, and puts risk analysis at the center of each loop. That makes it a natural home for security risk assessment, and it is often cited as the forerunner of iterative development. Other historic approaches that may appear on the exam include rapid application development (RAD), which emphasizes fast prototyping with user feedback, and the cleanroom method, which aims to prevent defects through formal specification and statistical testing rather than removing them through debugging.
Agile methods
Agile methods, crystallized in the Agile Manifesto of 2001, deliver working software in short iterations, welcome changing requirements and value collaboration over comprehensive documentation. Scrum organizes work in sprints, usually two weeks long, with a product owner who prioritizes a backlog, a development team and a Scrum Master who removes impediments. Kanban visualizes work on a board and limits work in progress rather than using fixed iterations. Extreme Programming (XP) contributed practices such as pair programming, test-driven development and continuous integration.
Agile creates both opportunities and risks for security. The opportunities are frequent feedback, small changes that are easier to review, and the ability to respond quickly to new threats. The risks are that security work is squeezed out of sprints in favor of visible features, that documentation needed for compliance is neglected, and that no one owns architecture-level security across many small teams. Security fits agile when it is expressed in agile terms: security requirements as backlog items or acceptance criteria, security criteria in the definition of done, lightweight threat modeling in sprint planning, security champions in each team and automated checks that run on every change.
| Agile element | How security is integrated |
|---|---|
| Product backlog | Security stories and non-functional requirements prioritized alongside features; security debt tracked visibly |
| User story | Security acceptance criteria and abuse cases attached to the story |
| Sprint planning | Lightweight threat modeling for stories that cross trust boundaries |
| Definition of done | Peer review, automated scans passed, security tests written, no new critical findings |
| Sprint review and retrospective | Security findings and near misses discussed; process improvements agreed |
| Team roles | A security champion in each team; product owner accountable for security risk decisions |
DevOps and DevSecOps
DevOps joins development and operations into a single flow, supported by automation, shared responsibility and fast feedback. Code moves through continuous integration (every change is merged frequently and built and tested automatically) and continuous delivery or deployment (every change that passes the pipeline is ready to release, or is released automatically). Infrastructure is defined as code, environments are created on demand, and teams own their services in production. High-performing DevOps organizations release many times a day with low change failure rates, as the research popularized by the DORA program has shown.
DevSecOps adds security as an equal, automated participant in that flow. Instead of a separate security phase, security checks run inside the pipeline: secrets scanning and static analysis when code is committed, software composition analysis when dependencies change, infrastructure-as-code scanning before environments are created, dynamic tests against staging environments, container image scanning before deployment, and runtime monitoring afterwards. The security team's role shifts from performing reviews to building and tuning these automated guardrails, coaching teams and handling the exceptions that automation cannot decide.
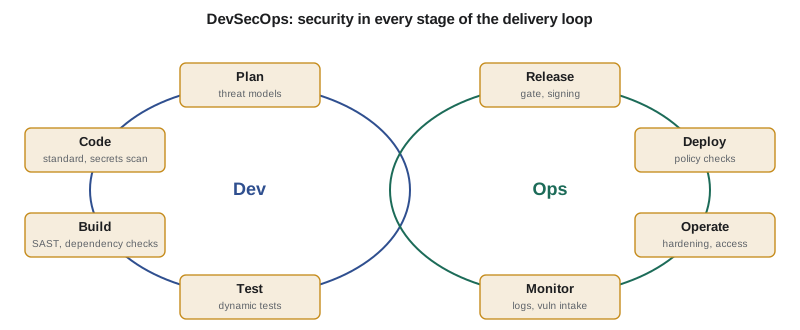
Automation brings speed and consistency, but it does not remove the need for judgment. Tools generate false positives that waste developer time and false negatives that create false confidence. Business logic flaws, authorization errors and design weaknesses are poorly detected by automated scanners. A DevSecOps program therefore combines automated checks for the common, well-defined problems with human threat modeling and review for the subtle ones, and it measures both.
Change management in development
Change management, introduced in CISSP-116 for operations and in ITIL-140 for service management, applies equally to software. Every change to production code should be traceable from a request or story, through review and testing, to an approved release, and it should be possible to roll back. In DevOps environments, much of this control is automated: branch protection rules require peer review before merging, the pipeline records who changed what and which tests passed, and deployment tools keep previous versions available for rollback. Auditors increasingly accept such automated evidence in place of manual change tickets, provided the controls cannot be bypassed and exceptions are recorded. Separation of duties is preserved by ensuring that no single person can write, approve and deploy a change alone.
Operations and maintenance are part of the development life cycle. Once software is live, the team must handle vulnerability reports, apply patches to its own code and dependencies, respond to incidents and keep configuration under control. Software that is released but not maintained decays: new vulnerabilities are discovered in its components, cryptographic choices become obsolete and the people who understood it move on.
Integrated product teams and the IPT idea
The CISSP outline also mentions integrated product teams (IPT), a term from systems engineering for cross-functional teams that bring together all disciplines needed to deliver a product, including engineering, testing, operations, security, procurement and the customer. The idea anticipates DevOps: security is a member of the team from the start rather than a reviewer at the end. In exam scenarios, a recommendation to involve security staff in project teams from inception is almost always better than one that adds a review at the end.
Maturity models and frameworks
Maturity models describe a progression from ad hoc to optimized practice and let organizations assess where they stand and plan improvement. The Capability Maturity Model Integration (CMMI), originally from Carnegie Mellon's Software Engineering Institute and now maintained by the ISACA-owned CMMI Institute, uses five levels: initial, managed, defined, quantitatively managed and optimizing. On the exam, remember the order and the idea that higher levels mean processes that are documented, measured and continuously improved.
| Model or framework | Owner | What it is | Typical use |
|---|---|---|---|
| CMMI | CMMI Institute (ISACA) | Five-level process maturity model | General process improvement and appraisal |
| OWASP SAMM | OWASP (open) | Software Assurance Maturity Model: 15 security practices in five business functions, each scored 0 to 3 | Self-assessment and roadmap for a secure development program |
| BSIMM | Black Duck (formerly Synopsys) | Building Security In Maturity Model: describes activities observed in real organizations, published in periodic reports | Benchmarking against peers |
| NIST SSDF | NIST (SP 800-218) | Secure Software Development Framework: high-level practices grouped as Prepare, Protect, Produce and Respond | Common vocabulary and baseline; referenced by US government guidance |
| ISO/IEC 27034 | ISO/IEC | Application security standard built on organizational and application normative frameworks | Formal, standards-based programs |
OWASP SAMM is prescriptive: it says what an organization should do at each level for each practice, which makes it convenient for building a roadmap. BSIMM is descriptive: it reports what many real organizations actually do, which makes it convenient for benchmarking. The NIST Secure Software Development Framework (SSDF) is outcome-based and deliberately technology-neutral. Version 1.1, published in February 2022 as SP 800-218, organizes practices into four groups: prepare the organization (PO), protect the software (PS), produce well-secured software (PW) and respond to vulnerabilities (RV). NIST released a draft of version 1.2 (SP 800-218 Rev. 1) for public comment in December 2025, adding practices such as PO.6; check NIST's site for its final status, which we could not confirm in October 2026. NIST also finalized SP 800-218A in 2024, a community profile that adds practices for developing generative AI and dual-use foundation models.
# OWASP SAMM-style self-assessment: current vs target scores (0-3) by business function
current = {
    'Governance':     {'Strategy and metrics': 1.0, 'Policy and compliance': 1.5, 'Education and guidance': 1.0},
    'Design':         {'Threat assessment': 0.5, 'Security requirements': 1.0, 'Security architecture': 1.5},
    'Implementation': {'Secure build': 2.0, 'Secure deployment': 2.0, 'Defect management': 1.0},
    'Verification':   {'Architecture assessment': 0.5, 'Requirements-driven testing': 1.0, 'Security testing': 1.5},
    'Operations':     {'Incident management': 1.5, 'Environment management': 2.0, 'Operational management': 1.5},
}
target = 2.0   # bank partner expectation for every practice within 18 months
print(f"{'Function':15s} {'avg':>4s}  largest gap")
gaps = []
for func, practices in current.items():
    avg = sum(practices.values()) / len(practices)
    worst = min(practices, key=practices.get)
    print(f'{func:15s} {avg:4.2f}  {worst} ({practices[worst]:.1f})')
    gaps += [(target - s, func, p) for p, s in practices.items() if s < target]
print(f'Practices below target: {len(gaps)} of 15')
print('Three largest gaps:')
for g, func, p in sorted(gaps, reverse=True)[:3]:
print(f' {p} ({func}): {g:.1f} levels')Function avg largest gap Governance 1.17 Strategy and metrics (1.0) Design 1.00 Threat assessment (0.5) Implementation 1.67 Defect management (1.0) Verification 1.00 Architecture assessment (0.5) Operations 1.67 Incident management (1.5) Practices below target: 12 of 15 Three largest gaps: Architecture assessment (Verification): 1.5 levels Threat assessment (Design): 1.5 levels Requirements-driven testing (Verification): 1.0 levels
The assessment shows a familiar pattern for a fast-growing company: strong automation in build and deployment, weak design-phase practices. Ridgeline builds and ships well but rarely models threats or reviews architecture. The roadmap that follows should therefore prioritize threat assessment and architecture assessment, which also address the bank partner's specific request for design evidence.
Worked problem
Choosing between SAMM and BSIMM for Ridgeline
Ridgeline's chief information security officer must show the bank partner a credible improvement plan and wants a maturity model to structure it. The board also wants to know how Ridgeline compares with similar firms.
Show solution
- For the improvement plan, SAMM is the better fit: it is free, prescriptive and produces practice-by-practice targets that translate directly into a roadmap.
- For peer comparison, BSIMM data shows which activities are common among participating firms, including financial services firms, so it answers the board's benchmarking question.
- Map both to the NIST SSDF, which many customers and US government buyers use as a common vocabulary, so the evidence can be reused in questionnaires.
- Repeat the SAMM assessment every six months and report progress to the board alongside a few outcome metrics, described in Lesson 12.
Answer: Use SAMM to plan, BSIMM to benchmark and the SSDF as a shared vocabulary, and report progress against all three with real outcome metrics.
Maturity scores are means, not ends. An organization can reach high scores by producing documents while its software remains vulnerable. Assessments should be backed by evidence and paired with outcome measures such as the number of serious vulnerabilities found in production and how quickly they are fixed.
Common mistakes
MistakeAssuming agile teams cannot meet compliance requirements.
InsteadExpress security as backlog items, acceptance criteria and definition-of-done criteria, and use pipeline records as evidence.
MistakeBelieving automated pipeline scanners make human review unnecessary.
InsteadCombine automation for common flaws with threat modeling and expert review for design and logic issues.
MistakeAllowing one engineer to write, approve and deploy a production change.
InsteadEnforce peer review and separation of duties through branch protection and pipeline controls.
MistakeConfusing BSIMM and SAMM.
InsteadSAMM is prescriptive and open; BSIMM is descriptive and based on observed activities.
MistakeTreating a maturity score as proof of secure software.
InsteadPair maturity assessments with evidence and outcome metrics.
MistakeAdding security reviewers only at the end of a project.
InsteadInclude security in integrated product teams from inception.
Summary and key terms
- Waterfall offers predictability and documentation but late feedback; the V-model pairs each phase with testing; the spiral model centers on risk analysis.
- Agile methods deliver in short iterations; security fits through backlog items, acceptance criteria, the definition of done and champions.
- DevOps automates integration and delivery; DevSecOps builds security checks into the pipeline while keeping human judgment for design and logic.
- Change management in development relies on traceability, peer review, separation of duties and rollback, often evidenced automatically.
- CMMI has five levels: initial, managed, defined, quantitatively managed and optimizing.
- OWASP SAMM is prescriptive, BSIMM is descriptive, and the NIST SSDF groups practices as Prepare, Protect, Produce and Respond.
- Maturity scores should be backed by evidence and outcome metrics.
- Waterfall model
- A sequential development model in which each phase is completed before the next begins.
- Spiral model
- An iterative model with risk analysis at the center of each cycle.
- Scrum
- An agile framework using sprints, a product backlog, a product owner and a Scrum Master.
- DevSecOps
- DevOps practice in which security checks and responsibilities are built into the automated delivery flow.
- Continuous integration
- Frequently merging changes, each automatically built and tested.
- CMMI
- Capability Maturity Model Integration, a five-level process maturity model.
- OWASP SAMM
- The Software Assurance Maturity Model, a prescriptive open model of 15 security practices.
- NIST SSDF
- The Secure Software Development Framework in NIST SP 800-218.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name one strength and one weakness of waterfall for security.
Show answer
Strength: documentation and formal reviews. Weakness: late feedback and rigidity.
What does the V-model add to waterfall?
Show answer
A verification phase paired with each development phase.
Which model puts risk analysis at the center of every cycle?
Show answer
The spiral model.
How can security requirements appear in Scrum?
Show answer
As backlog items, acceptance criteria and definition-of-done criteria.
Give three security checks that can run in a CI/CD pipeline.
Show answer
Secrets scanning, static analysis, software composition analysis, infrastructure-as-code scanning, dynamic testing or image scanning.
Why does DevSecOps still need human review?
Show answer
Scanners miss design flaws, business logic errors and many authorization problems.
List the five CMMI levels in order.
Show answer
Initial, managed, defined, quantitatively managed, optimizing.
What is the difference between SAMM and BSIMM?
Show answer
SAMM prescribes what to do; BSIMM describes what organizations actually do.
What are the four SSDF practice groups?
Show answer
Prepare the organization, protect the software, produce well-secured software, respond to vulnerabilities.
What is an integrated product team?
Show answer
A cross-functional team that includes all disciplines, including security, from the start.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.